Page: 1
/ 14
Total 190 questions
Cisco Securing Email with Cisco Secure Email Gateway 300-720 SESA Exam Questions
Question 1
An organization wants to use DMARC to improve its brand reputation by leveraging DNS records.
Which two email authentication mechanisms are utilized during this process? (Choose two.)
Answer : A, C
https://www.cisco.com/c/en/us/products/security/what-is-dmarc.html
SPF (Sender Policy Framework) and DKIM (DomainKeys Identified Mail) are two email authentication mechanisms that are utilized during this process. SPF and DKIM allow the domain owner to publish DNS records that specify the authorized IP addresses or hosts for sending emails from that domain and sign the messages with a cryptographic key to prove their authenticity and integrity.
DMARC (Domain-based Message Authentication, Reporting and Conformance) is an email authentication standard that builds on SPF and DKIM and allows the domain owner to publish DNS records that specify how receivers should handle messages that fail SPF or DKIM verification, such as reject, quarantine, or none, and how to report back the results of DMARC validation.
The other options are not valid email authentication mechanisms that are utilized during this process, because they are not part of DMARC standard.
Question 2
A network administrator notices that there are a high number of queries to the LDAP server. The mail logs show an entry ''550 Too many invalid recipients | Connection closed by foreign host.''
Which feature must be used to address this?
Answer : A
https://www.cisco.com/c/en/us/td/docs/security/esa/esa12-0/user_guide/b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_12_0_chapter_011010.html
DHAP (Directory Harvest Attack Prevention) is a feature that must be used to address this issue. DHAP is a mechanism that allows Cisco ESA to prevent directory harvest attacks, which are attempts by spammers or hackers to obtain valid email addresses from an LDAP server by sending messages with random or guessed recipients and checking for bounce messages.
To enable DHAP on Cisco ESA, the network administrator can follow these steps:
Select Network > Listeners and click Edit Settings for the listener that receives incoming messages.
Under SMTP Authentication Settings, select Enable Directory Harvest Attack Prevention.
Enter a value for Maximum Invalid Recipients per Hour, which is the number of invalid recipients that triggers DHAP.
Enter a value for Block Sender for (hours), which is the duration that Cisco ESA blocks messages from senders who exceed the maximum invalid recipients per hour.
Click Submit.
Question 3
An engineer must configure an incoming antispam mail policy in Cisco Secure Email Gateway for IT users. The solution must meet these requirements: *The policy must be editable only by administrators.
*The policy must be activated for all incoming emails that are destined for admin@cisco.com.
These configurations have been performed already:
*Create an incoming mail policy.
*Set the name and the role to admin.
*Activate the antispam security service.
Which two additional actions must be taken to complete the configuration? (Choose two.)
Answer : A, C
Question 4
Refer to the exhibit.
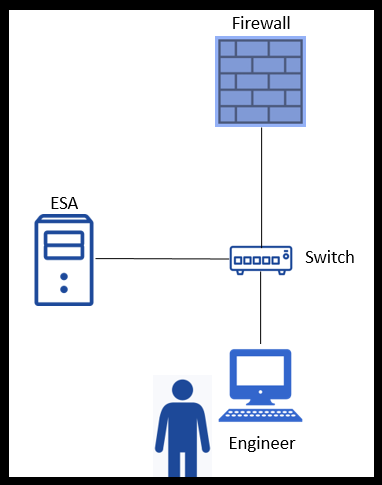
Refer to the exhibit. An engineer is trying to connect to a Cisco ESA using SSH and has been unsuccessful. Upon further inspection, the engineer notices that there is a loss of connectivity to the neighboring switch.
Which connection method should be used to determine the configuration issue?
Answer : D
Serial connection is a method that should be used to determine the configuration issue when there is a loss of connectivity to the neighboring switch. Serial connection allows the engineer to access the Cisco ESA console port using a serial cable and a terminal emulator, such as PuTTY or HyperTerminal, without relying on the network connectivity.
The other options are not valid methods to determine the configuration issue when there is a loss of connectivity to the neighboring switch, because they require network connectivity to work.
Question 5
Refer to the exhibit.
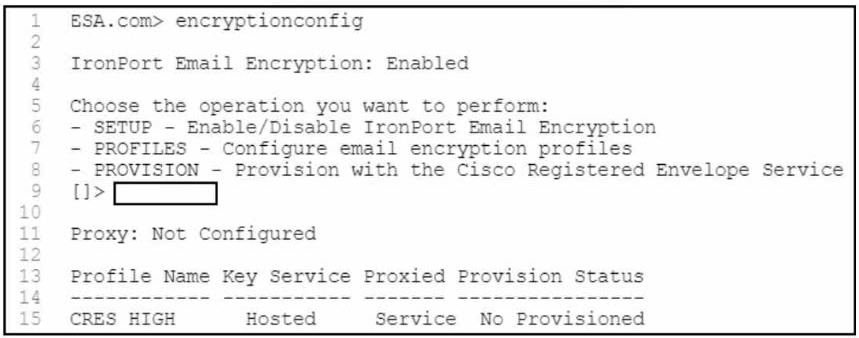
Refer to the exhibit. A security engineer must configure a Cisco Secure Email Gateway to ensure that encryption is enabled and the configured profile is provisioned. Which command must be used?
Answer : C
Question 6
An engineer must configure Directory Harvest Attack Prevention for SMTP in Cisco Secure Email Gateway. This error message must be sent when the listener receives more than 50 invalid
recipients per hour.
*500 - Too many requests
*Max. Invalid Recipients Per Hour was set to 50 already.
Which two actions must be taken next to set maximum invalid recipients per hour to meet the requirement? (Choose two.)
Answer : C, E
Question 7
What validates users via LDAP during login to end-user quarantine?
Answer : D
 All Official Question Types