Page: 1
/ 14
Total 345 questions
CompTIA SecurityX Certification Exam CAS-005 Practice Questions
Question 1
Which of the following most likely explains the reason a security engineer replaced ECC with a lattice-based cryptographic technique?
Answer : D
Question 2
A security analyst is reviewing the following code in the public repository for potential risk concerns:
typescript
CopyEdit
include bouncycastle-1.4.jar;
include jquery-2.0.2.jar;
public static void main() {...}
public static void territory() { ... }
public static void state() { ... }
public static String code = "init";
public static String access_token = "spat-hfeiw-sogur-werdb-werib";
Which of the following should the security analyst recommend first to remediate the vulnerability?
Answer : B
The code snippet exposes a hardcoded access token in a public repository. According to SecurityX CAS-005 secure coding best practices, the immediate action must be to revoke the exposed secret to prevent unauthorized access.
Removing the code from public view without revoking the token leaves the secret still usable by any attacker who has already seen or copied it.
SAST scanning would detect the issue but not mitigate it immediately.
Security awareness training is a long-term prevention measure but does not fix the immediate exposure.Revoking the secret first stops ongoing exploitation, after which the code can be removed, and preventative measures can be implemented.
Question 3
A company that relies on an COL system must keep it operating until a new solution is available Which of the following is the most secure way to meet this goal?
Answer : A
To ensure the most secure way of keeping a legacy system (COL) operating until a new solution is available, isolating the system and enforcing strict firewall rules is the best approach. This method minimizes the attack surface by restricting access to only the necessary endpoints, thereby reducing the risk of unauthorized access and potential security breaches. Isolating the system ensures that it is not exposed to the broader network, while firewall rules control the traffic that can reach the system, providing a secure environment until a replacement is implemented.
CompTIA SecurityX Study Guide: Recommends network isolation and firewall rules as effective measures for securing legacy systems.
NIST Special Publication 800-82, 'Guide to Industrial Control Systems (ICS) Security': Advises on isolating critical systems and using firewalls to control access.
'Network Security Assessment' by Chris McNab: Discusses techniques for isolating systems and enforcing firewall rules to protect vulnerable or legacy systems.
By isolating the system and implementing strict firewall controls, the organization can maintain the necessary operations securely while working on deploying a new solution.
Question 4
An organization with a remote workforce has a new client with the following requirements:
Consultants need to travel to the client site.
The company has proprietary information on its hard drives.
The company prohibits BYOD.
Which of the following would be the most beneficial for the organization to implement?
Answer : D
The best answer is D. Host-based encryption. The strongest clue is that the company has proprietary information on its hard drives and consultants must travel with company-managed devices because BYOD is prohibited. That makes protection of data at rest on the endpoint the primary concern. Host-based encryption protects the contents of the drive if a laptop is lost, stolen, or physically accessed during travel. CompTIA's SecurityX certification emphasizes building secure solutions across complex environments and supporting resilient enterprise protection, which includes securing endpoints and sensitive data stored on them.
Why the other options are not best:
A . Virtual hardware does not directly protect the data on the hard drive if the device is lost or stolen. B. Measured boot helps validate platform integrity at startup, but it does not primarily protect confidential data at rest. C. Secure enclave can protect certain secrets and key material, but it is narrower than full host-based encryption for an entire laptop drive. Because the requirement is specifically about proprietary data on traveling endpoints, full device or host-based encryption is the most beneficial control.
CompTIA SecurityX official certification page describing secure solution design across complex environments.
===========
Question 5
Which of the following best describes the challenges associated with widespread adoption of homomorphic encryption techniques?
Answer : D
Homomorphic encryption allows computations to be performed on encrypted data without decrypting it, providing strong privacy guarantees. However, the adoption of homomorphic encryption is challenging due to several factors:
A . Incomplete mathematical primitives: This is not the primary barrier as the theoretical foundations of homomorphic encryption are well-developed.
B . No use cases to drive adoption: There are several compelling use cases for homomorphic encryption, especially in privacy-sensitive fields like healthcare and finance.
C . Quantum computers not yet capable: Quantum computing is not directly related to the challenges of adopting homomorphic encryption.
D . Insufficient coprocessor support: The computational overhead of homomorphic encryption is significant, requiring substantial processing power. Current general-purpose processors are not optimized for the intensive computations required by homomorphic encryption, limiting its practical deployment. Specialized hardware or coprocessors designed to handle these computations more efficiently are not yet widely available.
CompTIA Security+ Study Guide
'Homomorphic Encryption: Applications and Challenges' by Rivest et al.
NIST, 'Report on Post-Quantum Cryptography'
Question 6
A company has the following requirements for a cloud-based web application:
* Must authenticate customers
* Must prevent data exposure
* Must allow customer access to data throughout the cloud environment
* Must restrict access by specific regions
Which of the following solutions best addresses these security requirements?
Answer : A
The best way to address these requirements is to apply Role-Based Access Controls (RBAC) combined with geolocation policies. RBAC ensures that customers are authenticated and authorized to access only the data they are entitled to, thereby minimizing data exposure risks. At the same time, geolocation policies enforce restrictions on which regions customers can access data from, helping with compliance requirements such as GDPR or regional sovereignty laws.
Option B (replicating data in each customer environment) is inefficient, expensive, and introduces additional risks related to data sprawl. Option C (regional hosting with unique links) complicates access management and does not inherently prevent exposure or enforce strong authentication. Option D (restricting to a single region provider) removes flexibility and may conflict with customer needs for global access.
Therefore, implementing RBAC along with geolocation controls provides fine-grained access management, ensures compliance, prevents unnecessary data exposure, and is scalable for a global cloud environment.
Question 7
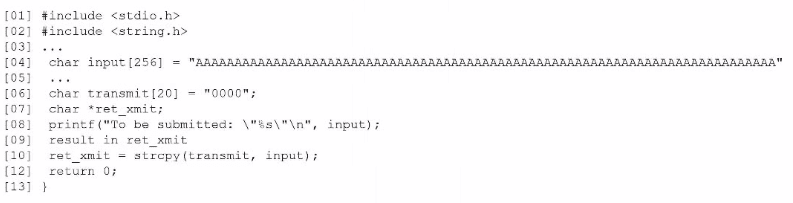
Based on the results of a SAST report on a legacy application, a security engineer is reviewing the following snippet of code flagged as vulnerable:
Which of the following is the vulnerable line of code that must be changed?
Answer : E
The vulnerability lies in line [10], where the function strcpy(transmit, input) is used. The strcpy function does not perform boundary checking when copying strings. Since input is defined with a size of 256 characters and transmit only has 20 characters allocated, the strcpy operation will cause a buffer overflow when the contents of input exceed the allocated size of transmit. This creates a significant security vulnerability, as attackers can overwrite adjacent memory, potentially injecting malicious code or altering program execution.
Lines [02], [04], [07], and [08] are not inherently vulnerable by themselves. Line [04] defines the oversized input, but the vulnerability only materializes when combined with the unsafe copy in line [10]. Secure coding practices recommend using safer alternatives like strncpy, which includes a length parameter, or implementing runtime checks to ensure the destination buffer size is not exceeded.
Thus, the vulnerable line that must be changed is line [10], where strcpy is used.
 All Official Question Types