Page: 1
/ 14
Total 254 questions
CompTIA Cloud+ (V4) CV0-004 Practice Questions
Question 1
Which of the following storage resources provides higher availability and speed for currently used files?
Answer : C
Hot storage using Solid State Drives (SSD) is designed for data that needs to be accessed frequently and quickly. SSDs provide faster access times compared to HDDs, making them suitable for high-availability and speed-critical files, such as those currently in use or requiring rapid access.
References: CompTIA Cloud+ resources and storage tiering concepts
Question 2
A security analyst reviews the daily logs and notices the following suspicious activity:

The analyst investigates the firewall logs and identities the following:

Which of the following steps should the security analyst take next to resolve this issue? (Select two).
Answer : B, D
Given the suspicious activity and Kali Linux's association with penetration testing and hacking tools, the security analyst should block all inbound connections on port 4444, as it is commonly used for malicious purposes, and block the IP address that's potentially the source of the intrusion. Additionally, checking the running processes on John Smith's computer is crucial to determine if a backdoor or unauthorized connection has been established.
: Incident response and threat mitigation steps such as these are part of the security protocols discussed in the CompTIA Cloud+ certification.
Question 3
An IT security team wants to ensure that the correct parties are informed when a specific user account is signed in. Which of the following would most likely allow an administrator to address this concern?
Answer : A
To ensure that the correct parties are informed when a specific user account is signed in, the best action is to create an alert based on user sign-in criteria. This alert can notify administrators or security personnel when the specified event occurs.
: Security monitoring and alerting are critical components of managing cloud environments securely, as discussed in the CompTIA Cloud+ certification.
Question 4
Which of the following are best practices when working with a source control system? (Select two).
Answer : A, E
Best practices when working with a source control system include merging code often to ensure that changes from different team members are integrated regularly, reducing integration issues. Committing code often is also recommended to save small changes frequently, which helps in tracking changes and resolving issues more effectively.
: Source control system best practices are part of the software development and deployment guidelines discussed in the CompTIA Cloud+ examination objectives.
Question 5
Which of the following cloud-native architecture designs is the most easily maintained, decentralized, and decoupled?
Answer : D
Microservices architecture is a design approach to build a single application as a suite of small services, each running in its own process and communicating with lightweight mechanisms, often an HTTP resource API. This design is decentralized and each service is fully decoupled, allowing for easier maintenance and scaling. Each microservice is built around a specific business capability and can be deployed independently, unlike monolithic architectures that are typically centralized and less flexible. References: CompTIA Cloud+ Study Guide (Exam CV0-004) - Chapter on Designing a Cloud Environment
Question 6
A cloud developer needs to update a REST API endpoint to resolve a defect. When too many users attempt to call the API simultaneously, the following message is displayed:
Error: Request Timeout - Please Try Again Later
Which of the following concepts should the developer consider to resolve this error?
Answer : C
To resolve the issue of a REST API endpoint timing out when too many users attempt to call the API simultaneously, the developer should consider implementing rate limiting. Rate limiting controls the number of requests a user can submit in a given amount of time, preventing overuse of the API resources and ensuring availability for all users. References: CompTIA Cloud+ Study Guide (Exam CV0-004) - Chapter on Cloud Service Maintenance and Management
Question 7
SIMULATION
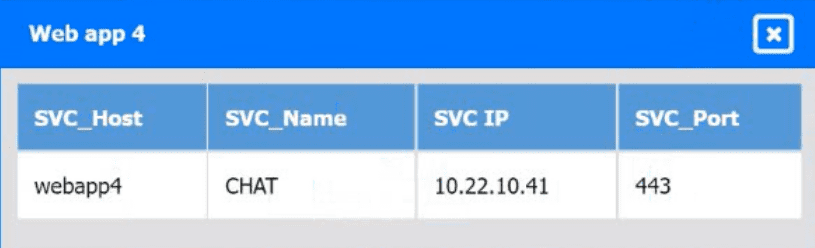
A company hosts various containerized applications for business uses. A client reports that one of its routine business applications fails to load the web-based login prompt hosted in the company cloud.
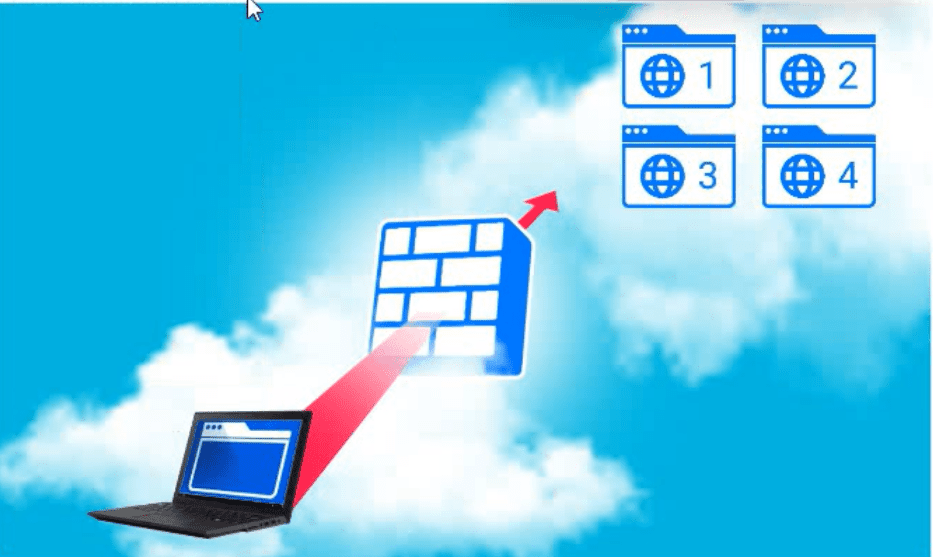
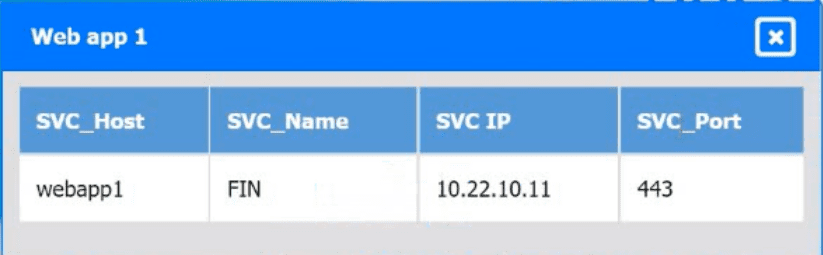
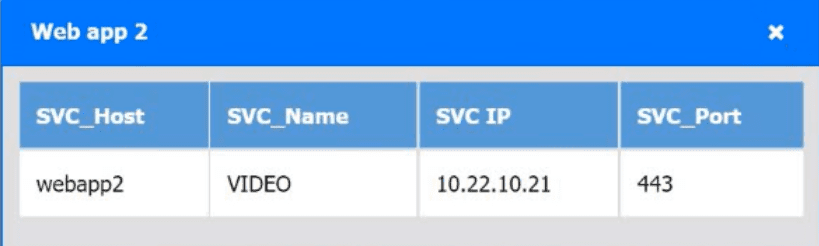
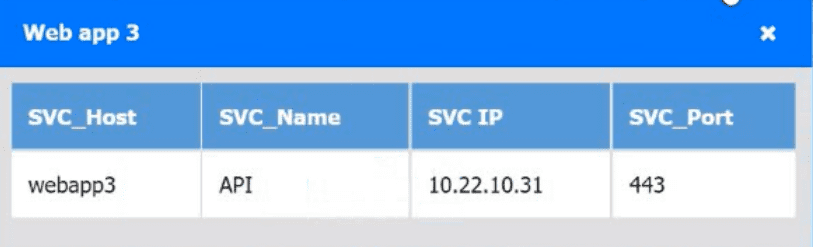
Click on each device and resource. Review the configurations, logs, and characteristics of each node in the architecture to diagnose the issue. Then, make the necessary changes to the WAF configuration to remediate the issue.

Answer : A
From the image, it's noticeable that some finance application rules are set to 'Block' traffic. If the client's issue is with a finance-related application not loading the login prompt, these rules could be the cause.
The rule with ID 1005, labeled 'Finance application 1', is configured to allow access to 'webapp1' for finance-related paths. However, rule 1006, labeled 'Finance application 2', is set to block access to 'webapp1' for login-related paths.
To remediate the issue based on the WAF configuration you have provided, you would want to:
Ensure that the correct paths to the finance application are allowed through the WAF.
Modify any rules that are incorrectly blocking access to the application.
If the client's problem is specifically with the login prompt, then rule 1006 seems the most likely culprit. Changing the action from 'Block' to 'Allow' for rule 1006 could potentially resolve the client's issue. The rule should be carefully reviewed and updated to ensure legitimate traffic is not being blocked while still protecting against unauthorized access.
 All Official Question Types