Page: 1
/ 14
Total 60 questions
CrowdStrike Certified Falcon Hunter CCFH-202b Exam Questions
Question 1
You would like to search for ANY process execution that used a file stored in the Recycle Bin on a Windows host. Select the option to complete the following EAM query.

Answer : B
This option is the correct one to complete the following EAM query:
event_simpleName=ProcessRollup2 FileName=$Recycle Bin
This query would search for any process execution that used a file stored in the Recycle Bin on a Windows host, as the asterisk (*) is a wildcard character that matches any number of characters before or after the specified string. The other options are not correct, as they use different wildcard characters that do not match the desired pattern.
Question 2
Refer to Exhibit.
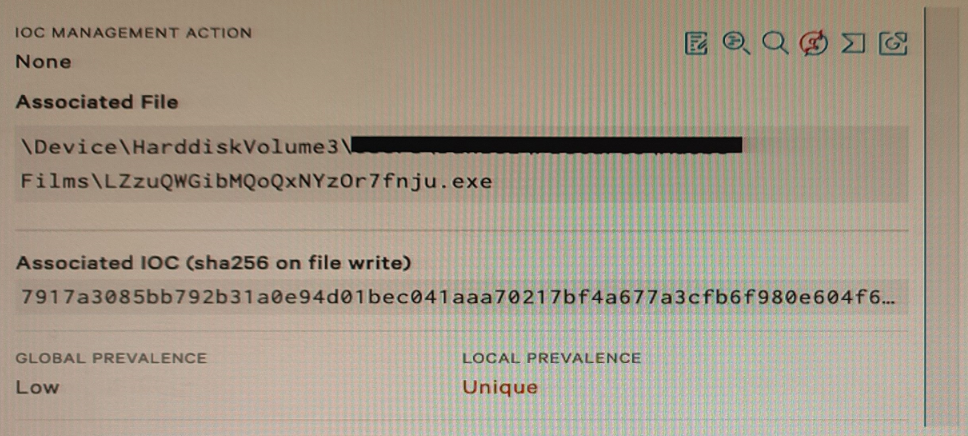
Falcon detected the above file attempting to execute. At initial glance; what indicators can we use to provide an initial analysis of the file?
Answer : B
The file name, path, Local and Global prevalence are indicators that can provide an initial analysis of the file without relying on external sources or tools. The file name can indicate the purpose or origin of the file, such as if it is a legitimate application or a malicious payload. The file path can indicate where the file was located or executed from, such as if it was in a temporary or system directory. The Local and Global prevalence can indicate how common or rare the file is within the environment or across all Falcon customers, which can help assess the risk or impact of the file.
Question 3
Which of the following best describes the purpose of the Mac Sensor report?
Answer : D
This is the correct answer for the same reason as above. The Mac Sensor report provides a comprehensive view of activities occurring on Mac hosts, including items of interest that may be hunting or investigation leads. It does not display a listing of all Mac hosts with or without a Falcon sensor installed, nor does it provide a detection focused view of known malicious activities occurring on Mac hosts.
Question 4
Which field should you reference in order to find the system time of a *FileWritten event?
Answer : A
ContextTimeStamp_decimal is the field that shows the system time of the event that triggered the sensor to send data to the cloud. In this case, it would be the time when the file was written. FileTimeStamp_decimal is the field that shows the last modified time of the file, which may not be the same as the time when the file was written. ProcessStartTime_decimal is the field that shows the start time of the process that performed the file write operation, which may not be the same as the time when the file was written. Timestamp is the field that shows the time when the sensor data was received by the cloud, which may not be the same as the time when the file was written.
Question 5
Which of the following does the Hunting and Investigation Guide contain?
Answer : C
The Hunting and Investigation guide contains example Event Search queries useful for threat hunting. These queries are based on common threat hunting use cases and scenarios, such as finding suspicious processes, network connections, registry activity, etc. The guide also explains how to customize and modify the queries to suit different needs and environments. The guide does not contain a list of all event types and their syntax, as that information is provided in the Events Data Dictionary. The guide also does not contain example Event Search queries useful for Falcon platform configuration, as that is not the focus of the guide.
Question 6
Which of the following is a suspicious process behavior?
Answer : D
Non-network processes are processes that are not expected to communicate over the network, such as notepad.exe. If they make an outbound network connection, it could indicate that they are compromised or maliciously used by an adversary. PowerShell running an execution policy of RemoteSigned is a default setting that allows local scripts to run without digital signatures. An Internet browser performing multiple DNS requests is a normal behavior for web browsing. PowerShell launching a PowerShell script is also a common behavior for legitimate tasks.
Question 7
Which pre-defined reports offer information surrounding activities that typically indicate suspicious activity occurring on a system?
Answer : B
Hunt reports are pre-defined reports that offer information surrounding activities that typically indicate suspicious activity occurring on a system. They are based on common threat hunting use cases and queries, and they provide visualizations and summaries of the results. Hunt reports can help threat hunters quickly identify and investigate potential threats in their environment.
 All Official Question Types