Page: 1
/ 14
Total 200 questions
EC-Council Certified SOC Analyst CSA v2 312-39 Exam Questions
Question 1
David Reynolds, a SOC analyst at a healthcare organization, is investigating suspicious login attempts flagged by the SIEM. To mitigate brute-force risk on targeted endpoints, he collaborates with IT to implement an automatic account lockout policy that temporarily disables accounts after multiple failed login attempts. Within the SOC's eradication strategy, which category of measures does this action align with?
Answer : D
Account lockout is an identity control that directly strengthens authentication by limiting repeated password guessing attempts. It sits within authentication and authorization measures because it governs how accounts can authenticate and how access is granted or denied based on login outcomes. In SOC terms, brute-force attacks target the authentication surface; lockout policies reduce attacker attempts and can prevent successful compromise by forcing a pause or administrative intervention after repeated failures. While the policy may be implemented on hosts or via directory services, its purpose is to control identity access behavior, not network segmentation or physical protections. Host security measures typically refer to endpoint hardening, patching, EDR controls, and local configuration baselines. Network security measures include firewall rules, segmentation, and traffic filtering. Physical security includes facility and device access controls. Because the action is specifically about controlling login attempts and access to accounts, it is best categorized as authentication and authorization. In practice, SOC teams complement lockout policies with MFA, conditional access, password spraying detection, and monitoring for ''failures followed by success'' patterns to reduce both brute-force success and user disruption.
Question 2
Bob is a SOC analyst in a multinational corporation that relies on a centralized file-sharing system for storing confidential project documents. One morning, he notices that a few critical financial records stored on the shared server appear to have been altered without authorization. Version history confirms unexpected changes made outside business hours. Bob must investigate by inspecting logs. Which log should he check to determine who accessed the files and when the modifications occurred?
Answer : A
Security logs are the primary source for auditing access and changes to protected objects, including files and folders, when file auditing is enabled. In Windows environments, this typically maps to ''Object Access'' auditing, which can record who accessed a file, what type of access was attempted (read, write, delete), and when it occurred. For a SOC analyst investigating unauthorized modifications, the goal is attribution (which user/account), timing (outside business hours), and action (write/modify/delete). Authentication logs show who logged in and from where, but they don't reliably indicate which file was modified unless correlated with object access events. Firewall and general network logs can help confirm remote access paths or suspicious connections, but they won't provide authoritative ''who modified which file'' evidence. In practice, the SOC would validate that file/folder auditing is enabled on the file server and that relevant events are being collected centrally. Then they correlate file access/modify events with sign-in activity, source device, and any privilege escalation indicators. Because the question specifically asks for determining ''who accessed the files and when modifications occurred,'' Security logs are the most direct and forensically valuable option.
Question 3
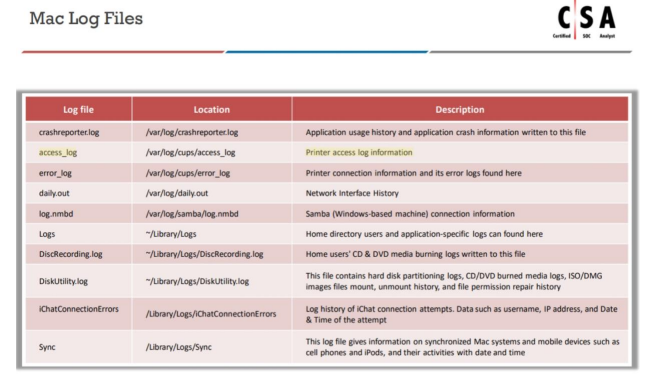
Which of the following directory will contain logs related to printer access?
Answer : B
Planning and budgeting:This is the initial phase where you determine the scope, objectives, and financial resources available for the lab.
Physical location and structural design considerations:Selecting a suitable location and designing the lab to meet operational needs and security requirements.
Work area considerations:Organizing the space efficiently for different tasks such as evidence analysis, storage, and administrative work.
Human resource considerations:Identifying the roles, responsibilities, and qualifications required for lab personnel.
Physical security recommendations:Implementing measures to protect sensitive data and physical assets within the lab.
Forensics lab licensing:Ensuring that the lab and its personnel are compliant with relevant laws, regulations, and industry standards.
References:While I can't refer to specific EC-Council SOC Analyst courses or study guides, these steps are generally accepted as part of the process for setting up a computer forensics lab. For detailed guidance, it's best to consult the official EC-Council resources and materials provided for the SOC Analyst certification.
Question 4
A multinational cybersecurity firm wants to enhance its threat intelligence capabilities by integrating real-time threat feeds into Microsoft Sentinel. These feeds include malicious IPs, domains, file hashes, and attack patterns. The firm requires a standardized protocol that allows automated threat intelligence sharing so Sentinel continuously receives updated indicators from external sources in a structured format. Which Microsoft Sentinel data connector should be implemented to integrate threat intelligence feeds using an industry-standard protocol?
Answer : C
TAXII (Trusted Automated eXchange of Indicator Information) is an industry-standard protocol for automated threat intelligence transport, commonly used alongside STIX-formatted threat data. The question explicitly requires a standardized protocol to automate sharing and continuously import structured threat indicators into Sentinel. The TAXII data connector is designed for this purpose: it enables pulling indicator data from TAXII servers so that malicious IPs, domains, and hashes can be ingested and used in detection and enrichment workflows. Syslog is a logging transport protocol for device and system logs, not threat intel sharing. Microsoft Defender for Cloud (Legacy) is unrelated to ingesting external threat feeds via a standardized intel protocol. The ''Threat Intelligence Platforms'' connector can be used to integrate certain TI sources, but the question specifically calls out using an industry-standard protocol for automated sharing, which is TAXII . From a SOC analyst perspective, using TAXII supports consistent ingestion, reduces manual indicator handling, and improves correlation by allowing Sentinel analytics rules and playbooks to leverage the latest indicators at scale.
Question 5
A SOC analyst receives an alert indicating that the system time on a critical Windows server was changed at 3:00 AM. There are no scheduled maintenance tasks at this time. Unauthorized time changes can be used to evade security controls, such as altering timestamps to obscure malicious activity. The analyst must identify the relevant event codes that log system time modifications and related suspicious behavior. Which of the following Windows Security Event Codes should the analyst review to investigate potential tampering?
Answer : C
Event ID 4616 is the key Windows Security log event for ''system time was changed,'' and it is the primary artifact to confirm and investigate time-tampering. It typically includes details such as the previous time, the new time, and the account or process context responsible, which helps the SOC determine whether the change was authorized (maintenance) or suspicious (off-hours, unusual account, unexpected host). Event ID 4618 is useful as a companion signal because it indicates monitored security-relevant conditions and can help reveal related suspicious behavior around auditing or security event patterns that may coincide with timestamp manipulation. In practice, SOC analysts correlate the time-change event with surrounding authentication events, privilege use, and process creation telemetry to identify the actor and intent. The other options do not directly target the time-change activity: 4608/4609 relate to system startup/shutdown; 4625 is failed logon and 4634 is logoff; 4624 is successful logon (useful context, but not the event that records the time modification itself). Therefore, the best pairing for investigating time tampering in the options provided is 4616 and 4618.
Question 6
A multinational financial institution notices unusual network activity during a routine security audit. The SOC detects multiple failed login attempts, followed by a successful access attempt using an administrator's credentials from an unrecognized IP address. Shortly after, sensitive customer records are accessed without authorization. The company suspects a breach and calls in the forensic investigation team. During evidence collection, the forensic team creates a detailed record that tracks every individual who handled the evidence, its storage location, and timestamps of transfers. What is this process called?
Answer : A
Chain of custody is the formal process used to document and preserve evidence integrity by recording who collected the evidence, who accessed it, where it was stored, and when it changed hands. In SOC and forensic operations, chain of custody is essential for maintaining evidentiary reliability, especially in cases with regulatory, legal, or disciplinary implications. It ensures that evidence has not been altered, tampered with, or mishandled, and it supports defensible conclusions about what occurred. Incident documentation is broader and includes timelines, decisions, actions taken, and communications, but it does not specifically track evidence handling transfers. Data imaging is the creation of a forensic copy of storage media (disk image), a separate technical step that may be recorded within chain-of-custody logs. Digital fingerprinting refers to generating hashes or other identifiers to confirm file integrity; again, it is a technique used within evidence handling, but the tracking record of handlers, locations, and transfers is chain of custody. For SOC analysts, correctly maintaining chain of custody is critical when responding to breaches involving sensitive customer records and potential compliance investigations.
Question 7
You are a Threat Hunter at a law firm that suffered a data breach where confidential documents were leaked. Using the Cyber Kill Chain framework, you trace the attacker's steps: they bypassed MFA by masquerading as a legitimate user, moved laterally, accessed sensitive records from a shared repository, and exfiltrated data over an extended period. You must identify the Cyber Kill Chain phase at which the attack was identified, to strengthen defenses and detect intrusions before exfiltration occurs. At which phase was the attack identified?
Answer : B
''Actions on objectives'' is the Cyber Kill Chain phase where the attacker achieves their mission goals---such as data theft, disruption, or destruction. In the scenario, the attacker accessed sensitive client records and exfiltrated them over time, which directly represents the adversary achieving the objective of obtaining confidential data. Delivery and exploitation occur earlier (initial delivery of a payload or credential capture and then exploiting access). Command and control is the stage where compromised systems communicate with attacker infrastructure to receive instructions, which may occur during lateral movement and persistence but is not the final objective. The scenario emphasizes that the breach was discovered after the attacker had already accessed the sensitive repository and exfiltrated data, meaning detection happened at or after the mission impact stage. From a SOC improvement perspective, the lesson is that detections should shift ''left'' in the kill chain: detect credential abuse, anomalous authentication, lateral movement, and suspicious access to file shares before exfiltration. But given where the investigation found the attacker's success, the correct phase is actions on objectives.
 All Official Question Types