Page: 1
/ 14
Total 201 questions
EC-Council Certified Security Analyst ECSA v10 ECSAv10 Exam Questions
Question 1
The first phase of the penetration testing plan is to develop the scope of the project in consultation with the client. Pen testing test components depend on the client's operating environment, threat perception, security and compliance requirements, ROE, and budget.
Various components need to be considered for testing while developing the scope of the project.
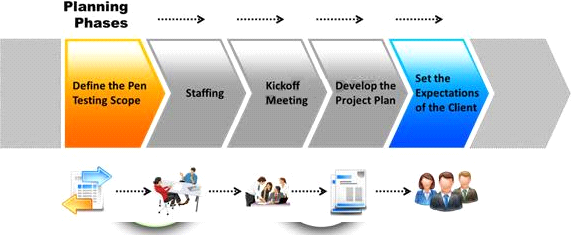
Which of the following is NOT a pen testing component to be tested?
Answer : C
Question 2
Jessica works as systems administrator for a large electronics firm. She wants to scan her network quickly todetect live hosts by using ICMP ECHO Requests. What type of scan is Jessica going to perform?
Answer : D
Question 3
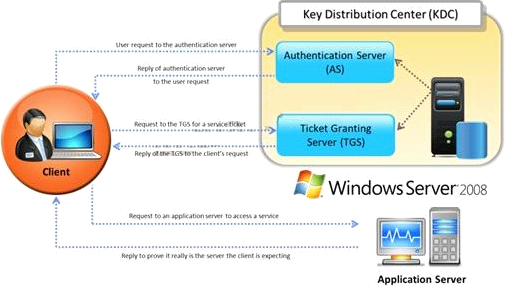
Identify the type of authentication mechanism represented below:
Answer : D
Question 4
You are carrying out the last round of testing for your new website before it goes live. The website has manydynamic pages and connects to a SQL backend that accesses your product inventory in a database. You comeacross a web security site that recommends inputting the following code into a search field on web pages tocheck for vulnerabilities:
When you type this and click on search, you receive a pop-up window that says: "This is a test."
What is the result of this test?
Answer : B
Question 5
Which one of the following 802.11 types uses either FHSS or DSSS for modulation?
Answer : D
Question 6
Hackers today have an ever-increasing list of weaknesses in the web application structure at their disposal, which they can exploit to accomplish a wide variety of malicious tasks.
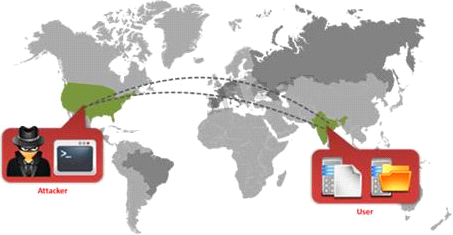
New flaws in web application security measures are constantly being researched, both by hackers and by security professionals. Most of these flaws affect all dynamic web applications whilst others are dependent on specific application technologies.
In both cases, one may observe how the evolution and refinement of web technologies also brings about new exploits which compromise sensitive databases, provide access to theoretically secure networks, and pose a threat to the daily operation of online businesses.
What is the biggest threat to Web 2.0 technologies?
Answer : A
Question 7
Identify the policy that defines the standards for the organizational network connectivity and security standards for computers that are connected in the organizational network.
Answer : C
 All Official Question Types