Page: 1
/ 14
Total 65 questions
Fortinet NSE 5 - FortiManager 7.6 Administrator FCP_FMG_AD-7.6 Exam Questions
Question 1
An administrator suspects that the Collector Agent is not forwarding login events to FortiGate.
What is the most effective troubleshooting step?
Answer : D
This point is not covered in the uploaded FortiManager 7.6 study guide, so the answer is based on Fortinet's official FSSO documentation. Fortinet documents that in FSSO Collector Agent deployments, the FortiGate connects to the Collector Agent on TCP port 8000 by default, and if a different port is not configured, that is the port that must be reachable. Fortinet also explains that the DC agents monitor user logon events and pass the information to the Collector Agent, which stores the information and sends it to the FortiGate.
So, when login events are not reaching FortiGate, the most effective first troubleshooting step is to verify connectivity on TCP 8000 between the Collector Agent and FortiGate. Options A, B, and C are less direct and do not test the actual transport path used by the Collector Agent to send FSSO information to FortiGate.
Question 2
Refer to the exhibits.
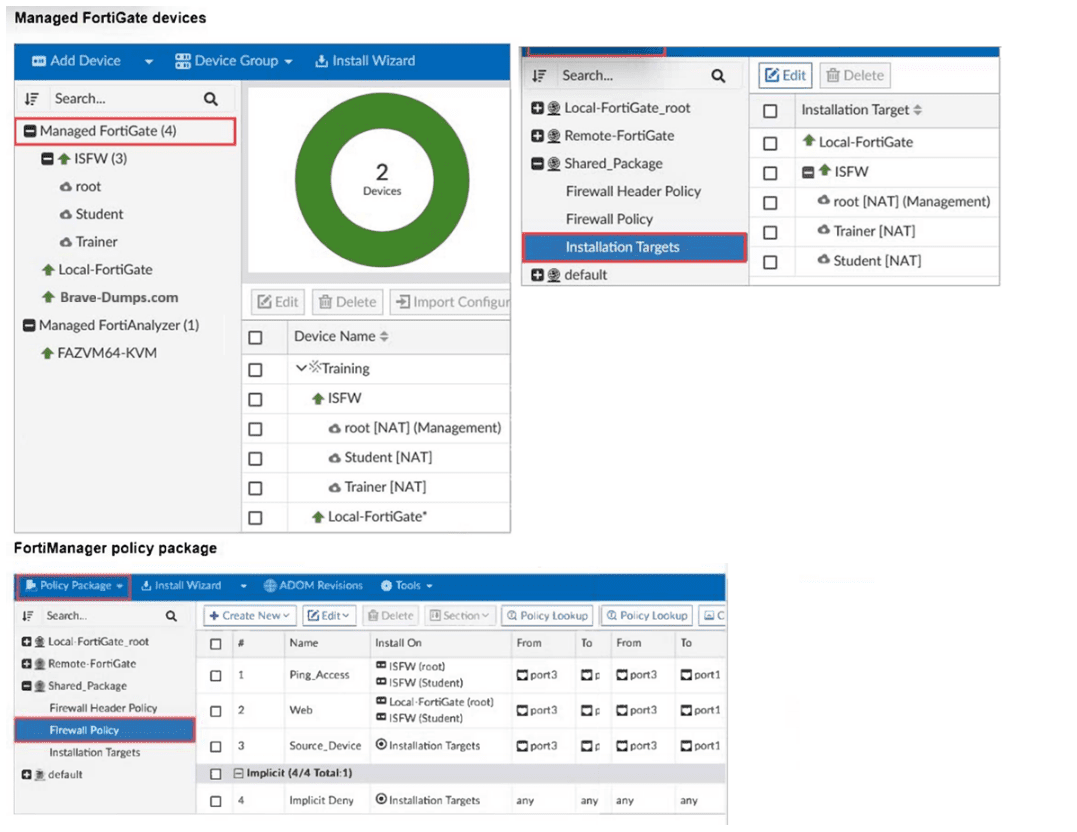
What can you conclude, based on the configuration shown in the exhibit? Choose one answer
Answer : A
The best conclusion is A. From the exhibit, B is clearly incorrect because policy sequence #1 Ping_Access is targeted to ISFW root and ISFW Student, not to root NAT and Trainer NAT. Also, C is incorrect because FortiManager allows a rule to inherit Installation Targets. The study guide explains that a policy package can target one or more devices or VDOMs, and the Install On column is used only for per-rule exceptions in a shared policy package. A rule does not need explicit devices listed if it is meant to apply to the package's installation targets.
D is also incorrect because global header policies are created in the Global Database ADOM and placed at the top only when a global package is assigned. The exhibit shows a shared policy package, not a global ADOM header-policy assignment.
=========
Question 3
What can you conclude from the failed installation log shown in the exhibit?

Answer : D
The correct answer is D. The lab guide explains that when an installation fails, the installation log shows the commands that the managed device received and accepted, as well as the commands that the managed device did not accept.
From the exhibit, FortiGate accepted the policy creation commands for policy ID 2 such as set srcintf port3, set dstintf port1, set srcaddr all, set dstaddr all, set action accept, and set schedule always. However, the line set users student failed with ''entry not found in datasource'' and ''value parse error before 'student'''. That shows the user reference was not accepted, while the rest of the policy commands were processed. Therefore, policy ID 2 is still created, but without the remote user student. This rules out A, B, and C.
=========
Question 4
An administrator upgrades FortiManager with workspace mode per ADOM enabled to the latest version but notices that the ADOM versions did not change.
Why were the ADOMs not upgraded?
Answer : B
The correct answer is B. The FortiManager 7.6 Administrator Study Guide gives the exact extract: ''Also note when you upgrade the FortiManager firmware version the existing ADOMs are not automatically upgraded.'' This directly explains why the administrator saw the FortiManager upgrade complete while the ADOM versions remained unchanged.
The same section also explains that ADOM upgrades are a separate action: ''You can upgrade an ADOM in System Settings > ADOMs'' and ''Can upgrade to one version higher at a time.'' In addition, the guide recommends: ''upgrade all devices first, and then upgrade the ADOM.''
So the issue is not workspace mode, locked ADOMs, or a stuck task. The ADOMs simply require their own manual upgrade step after the FortiManager firmware upgrade.
Question 5
Refer to the exhibit.

What percentage of the available RAM is being used by the process in charge of downloading the web and email filter databases from the public FortiGuard servers?
Answer : D
The correct answer is D. The FortiManager 7.6 Administrator Study Guide gives the exact extract under Web Filter and Email Filter: ''fgdlinkd --- Responsible for downloading web filter and email filter databases''. The same study guide section explains that the execute top command displays real-time CPU and RAM usage, and the %MEM column shows the memory percentage used by each process.
In the exhibit, the line for fgdlinkd shows %MEM 2.9. Therefore, the process responsible for downloading the web and email filter databases is using 2.9% of RAM. That matches option D exactly. The other values belong to different processes, such as fgdsvr and other FortiGuard-related daemons, but not the downloader process identified in the study guide.
=========
Question 6
Refer to the exhibit.
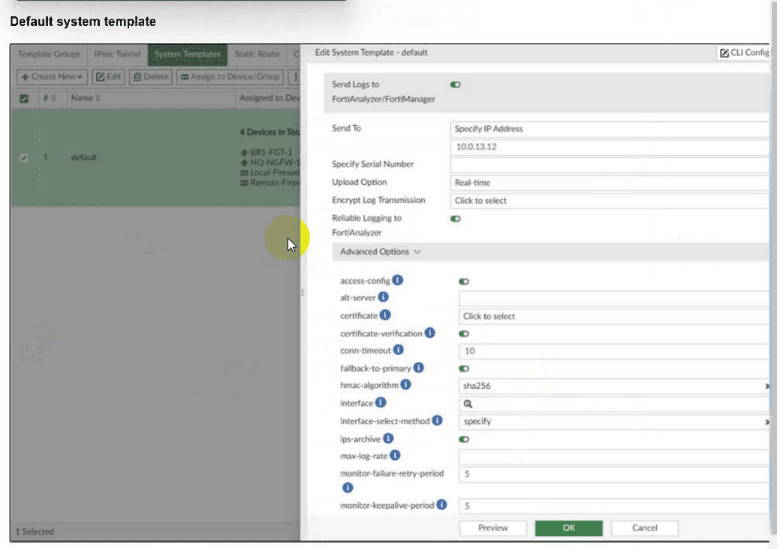
An administrator has assigned the default system template to install all devices with the FortiAnalyzer IP address 10.0.13.12. However, not all FortiGate devices can reach FortiAnalyzer using the default interface. Some devices may use the LAN interface, while others may use the WAN interface. How can the administrator change the source interface for FortiGate devices using the default system template? Choose one answer
Answer : B
The correct answer is B because FortiManager supports ADOM-level metadata variables in scripts and templates. The study guide explicitly states that meta fields cannot be used as variables in scripts or provisioning templates; instead, you must use ADOM-level metadata variables. It further says these variables can be used in templates, and their values can be mapped depending on the device where the template is applied.
That makes metadata variables the proper method for handling per-device differences such as whether a FortiGate should use a LAN or WAN source interface for FortiAnalyzer communication. A is wrong because per-device dynamic objects apply to objects like addresses and VIPs, not template interface selection. D is wrong because meta fields are comments/attributes, not template variables. C could work operationally, but it is not the FortiManager feature intended for this use case.
=========
Question 7
Which FortiGate configuration settings is part of an ADOM-level database on FortiManager?
Answer : B
The best verified answer is B. The FortiManager 7.6 Administrator Study Guide shows that the ADOM Layer contains Policy and Objects, and specifically states: ''Policy & Objects: Centralize the management of firewall policies, objects, and security profiles, among others.'' Because security-related policy settings belong to the Policy and Objects layer, they are part of the ADOM-level database.
By contrast, Routing and SNMP are treated as device-level settings. The lab guide shows Routing under the device/network configuration view, and SNMP as a setting in the system template that ''pushes configuration changes to the device level.''
Also, provisioning templates such as NSX-T service are listed as having precedence over device-layer configurations, which further indicates they are not the Policy and Objects ADOM database answer here.
=========
 All Official Question Types