Page: 1
/ 14
Total 183 questions
Fortinet NSE 4 - FortiOS 7.2 NSE4_FGT-7.2 Exam Questions
Question 1
Refer to the exhibit.
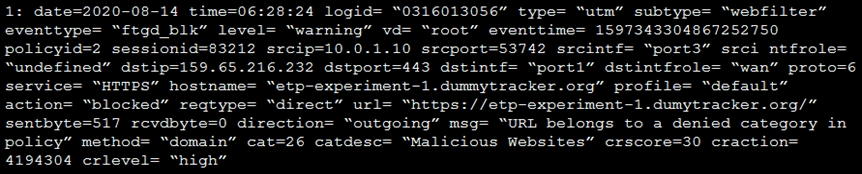
Based on the raw log, which two statements are correct? (Choose two.)
Answer : B, C
Question 2
If the Services field is configured in a Virtual IP (VIP), which statement is true when central NAT is used?
Answer : C
Question 3
Refer to the exhibit.
Refer to the FortiGuard connection debug output.
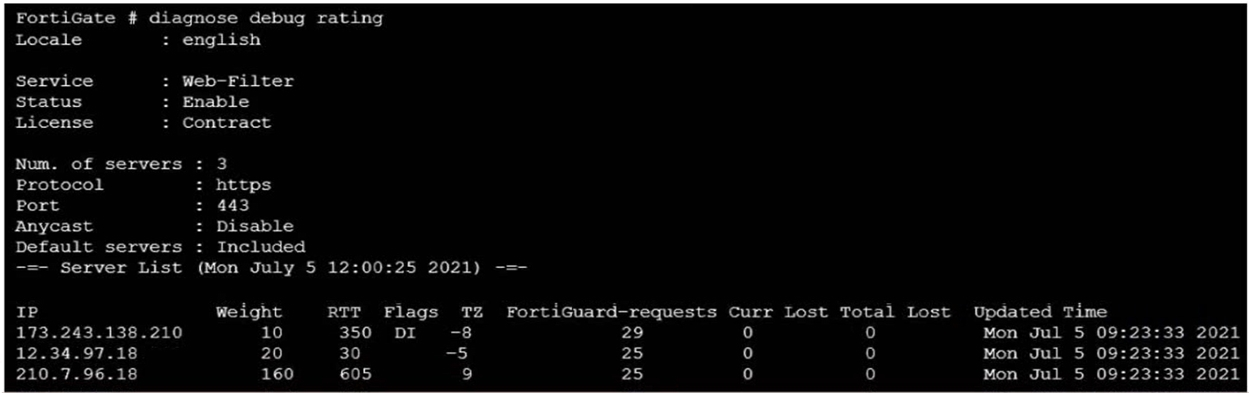
Based on the output shown in the exhibit, which two statements are correct? (Choose two.)
Answer : B, D
FortiGate Security 7.2 Study Guide (p.287-288): 'Flags: D (IP returned from DNS), I (Contract server contacted), T (being timed), F (failed)' 'By default, FortiGate is configured to enforce the use of HTTPS port 443 to perform live filtering with FortiGuard or FortiManager. Other ports and protocols are available by disabling the FortiGuard anycast setting on the CLI.'
Question 4
What are two functions of the ZTNA rule? (Choose two.)
Answer : B, D
A ZTNA rule is a policy that enforces access control and applies security profiles to protect traffic between the client and the access proxy1.A ZTNA rule defines the following parameters1:
Incoming interface: The interface that receives the client request.
Source: The address and user group of the client.
ZTNA tag: The tag that identifies the domain that the client belongs to.
ZTNA server: The server that hosts the access proxy.
Destination: The address of the application that the client wants to access.
Action: The action to take for the traffic that matches the rule. It can be accept, deny, or redirect.
Security profiles: The security features to apply to the traffic, such as antivirus, web filter, application control, and so on.
A ZTNA rule does not redirect the client request to the access proxy.That is the function of a policy route that matches the ZTNA tag and sends the traffic to the ZTNA server2.
A ZTNA rule does not define the access proxy.That is done by creating a ZTNA server object that specifies the IP address, port, and certificate of the access proxy3.
FortiGate Infrastructure 7.2 Study Guide (p.177): 'A ZTNA rule is a proxy policy used to enforce access control. You can define ZTNA tags or tag groups to enforce zero-trust role-based access. To create a rule, type a rule name, and add IP addresses and ZTNA tags or tag groups that are allowed or blocked access. You also select the ZTNA server as the destination. You can also apply security profiles to protect this traffic.'
Question 5
If the Issuer and Subject values are the same in a digital certificate, which type of entity was the certificate issued to?
Answer : D
Question 6
Consider the topology:
Application on a Windows machine <--{SSL VPN} -->FGT--> Telnet to Linux server.
An administrator is investigating a problem where an application establishes a Telnet session to a Linux server over the SSL VPN through FortiGate and the idle session times out after about 90 minutes. The administrator would like to increase or disable this timeout.
The administrator has already verified that the issue is not caused by the application or Linux server. This issue does not happen when the application establishes a Telnet connection to the Linux server directly on the LAN.
What two changes can the administrator make to resolve the issue without affecting services running through FortiGate? (Choose two.)
Answer : C, D
Question 7
Refer to the exhibit.
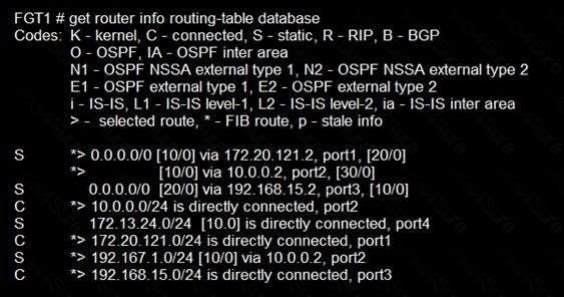
Given the routing database shown in the exhibit, which two statements are correct? (Choose two.)
Answer : B, C
https://community.fortinet.com/t5/FortiGate/Technical-Tip-How-to-identify-Inactive-Routes-in-the-Routing/ta-p/197595
 All Official Question Types