Page: 1
/ 14
Total 30 questions
Fortinet NSE 6 - FortiAnalyzer 7.2 Administrator NSE6_FAZ-7.2 Exam Questions
Question 1
Which statement is true about using aggregation mode on FortiAnalyzer?
Answer : B
In aggregation mode, FortiAnalyzer stores logs received from devices and forwards them at a specified time each day to avoid duplication. It is specifically designed to work between two FortiAnalyzer units and does not support syslog or CEF servers. Additionally, aggregation mode configurations are limited to CLI commands log-forward and log-forward-service. Reference: FortiAnalyzer 7.2 Administrator Guide, 'Aggregation' and 'CLI Commands for Aggregation Mode' sections.
Question 2
Which two methods can you use to restrict administrative access on FortiAnalyzer? (Choose two.)
Answer : A, B
To restrict administrative access on FortiAnalyzer, two effective methods are using administrator profiles and configuring trusted hosts. Administrator profiles allow for defining the level of access and permissions for different administrators, controlling what each administrator can see and do within the FortiAnalyzer unit. Configuring trusted hosts enhances security by limiting administrative access to specified IP addresses, ensuring that administrators can only connect from approved locations or networks, thus preventing unauthorized access from outside specified subnets or IP addresses. Reference: FortiAnalyzer 7.4.1 Administration Guide, 'Administrators' and 'Trusted hosts' sections.
Question 3
Refer to the exhibit.
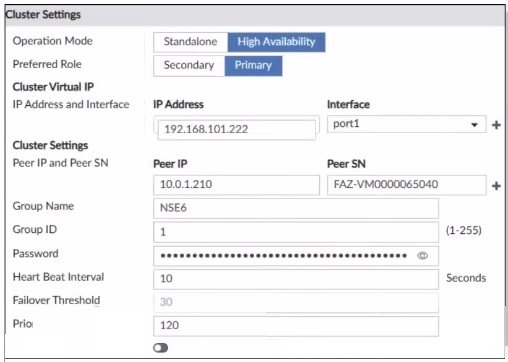
The image displays "he configuration of a FortiAnalyzer the administrator wants to join to an existing HA cluster.
What can you conclude from the configuration displayed?
Answer : D
The configuration displayed in the exhibit indicates that the FortiAnalyzer is set up with a cluster virtual IP address of 192.168.101.222 assigned to interface port1. This setup is typically used for the FortiAnalyzer to receive logs on that interface when operating in a High Availability (HA) configuration. The exhibit does not provide enough information to conclude whether this FortiAnalyzer will be the primary unit in the HA cluster or the duration for the failover trigger; it only confirms the interface configuration for log reception. Reference: Based on the FortiAnalyzer 7.4.1 Administration Guide, the similar configurations for HA and log reception are discussed, which would be relevant for understanding the settings in FortiAnalyzer 7.2.
Question 4
Which two statements about FortiAnalyzer operating modes are true? (Choose two.)
Answer : B, D
The default operating mode for FortiAnalyzer is analyzer mode. In this mode, FortiAnalyzer provides full functionality for event management and reporting features. This mode is intended for environments where comprehensive analysis and reporting are required. It allows FortiAnalyzer to collect, analyze, and store logs, as well as generate reports and manage events. Reference: FortiAnalyzer 7.4.1 Administration Guide, 'Operating modes' section.
Question 5
Which process caches logs on FortiGate when FortiAnalyzer is not readable?
Answer : A
The process logfiled in FortiGate units with an SSD disk is responsible for buffering logs when FortiAnalyzer is unreachable. If the connection to FortiAnalyzer is lost and the memory log buffer is full, logfiled allows logs to be buffered on disk. These logs are then sent to FortiAnalyzer once the connection is restored. This reliable logging mechanism ensures that logs are not lost during periods when FortiAnalyzer is not reachable, thereby maintaining log integrity and continuity. Reference: FortiOS 7.4.1 Administration Guide, 'Log Buffering' and 'Reliable Logging' sections.
Question 6
Which statement is true about ADOMs?
Answer : B
Regarding ADOMs (Administrative Domains) in FortiAnalyzer, a fabric ADOM is capable of including all device types that FortiAnalyzer supports. This is part of the flexibility offered by ADOMs to manage and report on logs from various devices within a Fortinet security fabric. ADOMs can be enabled to support non-FortiGate devices as well, and the root ADOM in Fabric ADOMs provides visibility into all Security Fabric devices. Additionally, it should be noted that in normal mode, you cannot assign different FortiGate VDOMs to different ADOMs, while in advanced mode, you can, which provides a more granular control over the log data from individual VDOMs. Reference: FortiAnalyzer 7.4.1 Administration Guide, 'ADOMs' and 'ADOM device modes' sections.
Question 7
What is true about a FortiAnalyzer Fabric?
Answer : D
In a FortiAnalyzer Fabric, the FortiAnalyzer can recognize a Security Fabric group of devices, and it supports the Security Fabric by storing and analyzing logs from these units as if they were from a single device. The members of the Security Fabric group send their logs to the FortiAnalyzer, which acts as a supervisor for log storage and analysis, providing a centralized point of visibility and control over the logs. Reference: FortiAnalyzer 7.4.1 Administration Guide, 'Security Fabric' section.
 All Official Question Types