Page: 1
/ 14
Total 80 questions
Fortinet NSE 7 - Enterprise Firewall 7.2 NSE7_EFW-7.2 Exam Questions
Question 1
Exhibit.
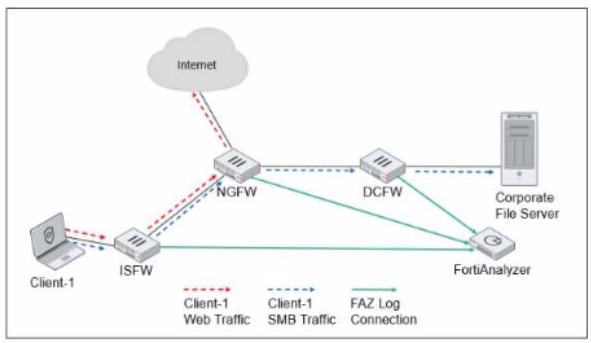
ISFW is installed in the access layer NGFW is performing SNAT and web tittering DCFW is running IPS Which two statements are true regarding the Security Fabric logging? (Choose two.)
Answer : A, B
Question 2
Winch two statements about ADVPN are true? (Choose two)
Answer : A, C
ADVPN (Auto Discovery VPN) is a feature that allows to dynamically establish direct tunnels (called shortcuts) between the spokes of a traditional Hub and Spoke architecture. The auto-discovery receiver must be set to enable on the spokes to allow them to receive NHRP messages from the hub and other spokes. NHRP (Next Hop Resolution Protocol) is used for on-demand tunnels, which are established when there is traffic between spokes. Routing is configured by enabling add-nhrp-route, not add-advpn-route.Reference:=ADVPN | FortiGate / FortiOS 7.2.0 | Fortinet Document Library,Technical Tip: Fortinet Auto Discovery VPN (ADVPN)
Question 3
An administrator is configuring two FortiGate devices in an HA cluster. While configuring the devices, the administrator issues the following commands on both HA cluster members:
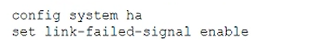
In which two ways do these commands impact the HA cluster? (Choose two.)
Answer : A, B
Question 4
You contoured an address object on the tool fortiGate in a Security Fabric. This object is not synchronized with a downstream device. Which two reasons could be the cause? (Choose two)
Answer : A, C
Option A is correct because the address object on the tool FortiGate will not be synchronized with the downstream devices if it has fabric-object set to disable.This option controls whether the address object is shared with other FortiGate devices in the Security Fabric or not1.
Option C is correct because the downstream FortiGate will not receive the address object from the tool FortiGate if it has fabric-object-unification set to local.This option controls whether the downstream FortiGate uses the address objects from the root FortiGate or its own local address objects2.
Option B is incorrect because the root FortiGate has configuration-sync set to enable by default, which means that it will synchronize the address objects with the downstream devices unless they are disabled by the fabric-object option3.
Option D is incorrect because the downstream FortiGate has configuration-sync set to local by default, which means that it will receive the address objects from the root FortiGate unless they are overridden by the fabric-object-unification option4.Reference: =
1: Group address objects synchronized from FortiManager5
2: Security Fabric address object unification6
3: Configuration synchronization7
4: Configuration synchronization7
: Security Fabric - Fortinet Documentation
Question 5
Which ADVPN configuration must be configured using a script on fortiManager, when using VPN Manager to manage fortiGate VPN tunnels?
Answer : A
To enable AD-VPN, you need to edit an SD-WAN overlay template and enable the Auto-Discovery VPN toggle. This will automatically add the required settings to the IPsec template and the BGP template. You cannot enable AD-VPN directly in the IPsec phase 1 settings using VPN Manager.Reference:=ADVPN | FortiManager 7.2.0 - Fortinet Documentation
Question 6
Exhibit.
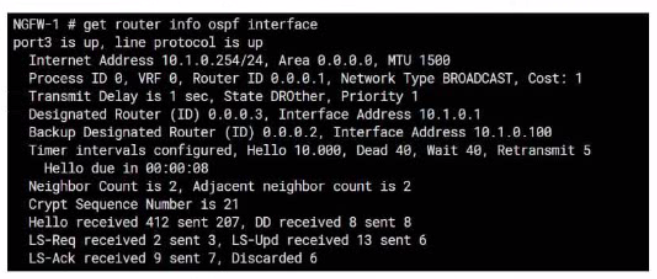
Refer to the exhibit, which shows information about an OSPF interlace
What two conclusions can you draw from this command output? (Choose two.)
Answer : A, C
From the OSPF interface command output, we can conclude that the port3 network has more than one OSPF router because the Neighbor Count is 2, indicating the presence of another OSPF router besides NGFW-1. Additionally, we can deduce that the interfaces of the OSPF routers match the MTU value configured as 1500, which is necessary for OSPF neighbors to form adjacencies. The MTU mismatch would prevent OSPF from forming a neighbor relationship.
Fortinet FortiOS Handbook: OSPF Configuration
Question 7
Which statement is true regarding the Bidirectional Forwarding Detection protocol in BGP?
Answer : C
 All Official Question Types