Page: 1
/ 14
Total 105 questions
Fortinet NSE 8 - Written NSE8_812 Exam Questions
Question 1
An administrator has configured a FortiGate device to authenticate SSL VPN users using digital certificates. A FortiAuthenticator is the certificate authority (CA) and the OCSP server.
Part of the FortiGate configuration is shown below:

Based on this configuration, which authentication scenario will FortiGate deny?
Answer : B
Question 2
Refer to the exhibit showing a firewall policy configuration.
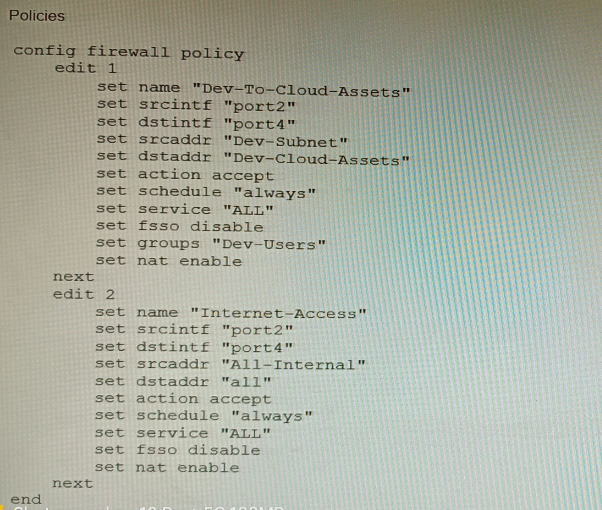
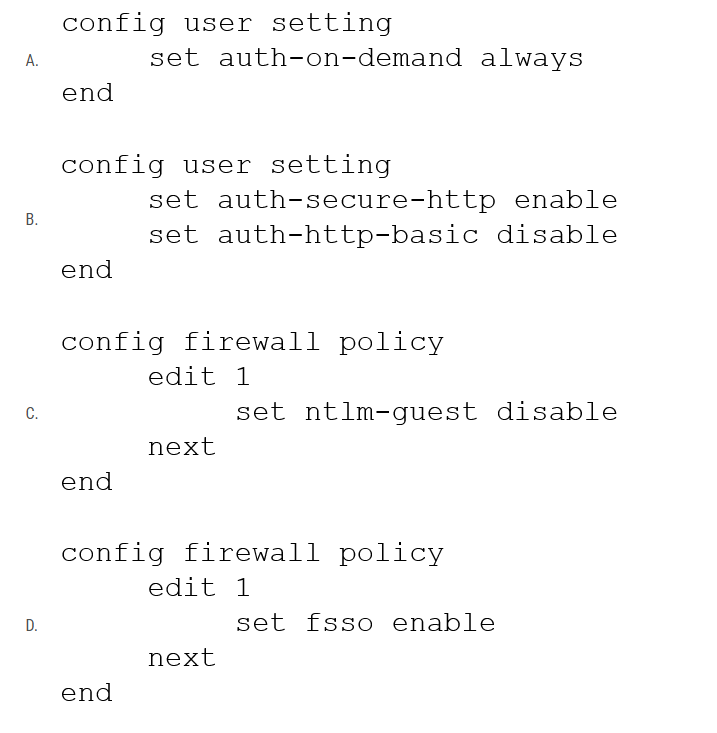
To prevent unauthorized access of their cloud assets, an administrator wants to enforce authentication on firewall policy ID 1.
What change does the administrator need to make?
Answer : A
https://docs.fortinet.com/document/fortigate/6.2.0/new-features/238665/authentication-policy-extensions
Question 3
Refer to the exhibit.

A customer is trying to setup a Playbook automation using a FortiAnalyzer, FortiWeb and FortiGate. The intention is to have the FortiGate quarantine any source of SQL Injection detected by the FortiWeb. They got the automation stitch to trigger on the FortiGate when simulating an attack to their website, but the quarantine object was created with the IP 0.0.0.0. Referring to the configuration and logs in the exhibits, which two statements are true? (Choose two.)
Answer : A, D
Question 4
Refer to the exhibit.

FortiManager is configured with the Jinja Script under CLI Templates shown in the exhibit.
Which two statements correctly describe the expected behavior when running this template? (Choose two.)
Answer : D, E
D . The administrator must first manually map the interface for each device with a meta field.
The Jinja template in the exhibit is expecting a meta field called WAN to be set on the managed FortiGate. This meta field will specify which interface on the FortiGate should be assigned the 'WAN' role. If the meta field is not set, then the template will fail.
E . The template will fail because this configuration can only be applied with a CLI or TCL script.
The Jinja template in the exhibit is trying to configure the interface role on the managed FortiGate. This type of configuration can only be applied with a CLI or TCL script. The Jinja template will fail because it is not a valid CLI or TCL script.
Question 5
A customer has FortiAP devices in three branch offices managed from a FortiGate in the HQ. Each FortiAP is connected to a dedicated management VLAN.
The customer wants the users connected to the FortiAP SSIDs to use the branch local internet connection, but each branch uses a different VLAN ID for the bridge. HQ users travel to different branches and connect to the same SSID.
Which configuration option will solve this requirement?
Answer : B
Question 6
Refer to the exhibits.

You are configuring a Let's Encrypt certificate to enable SSL protection to your website. When FortiWeb tries to retrieve the certificate, you receive a certificate status failed, as shown below.

Based on the Server Policy settings shown in the exhibit, which two configuration changes will resolve this issue? (Choose two.)
Answer : A, B
Question 7
Refer to the exhibit that shows VPN debugging output.
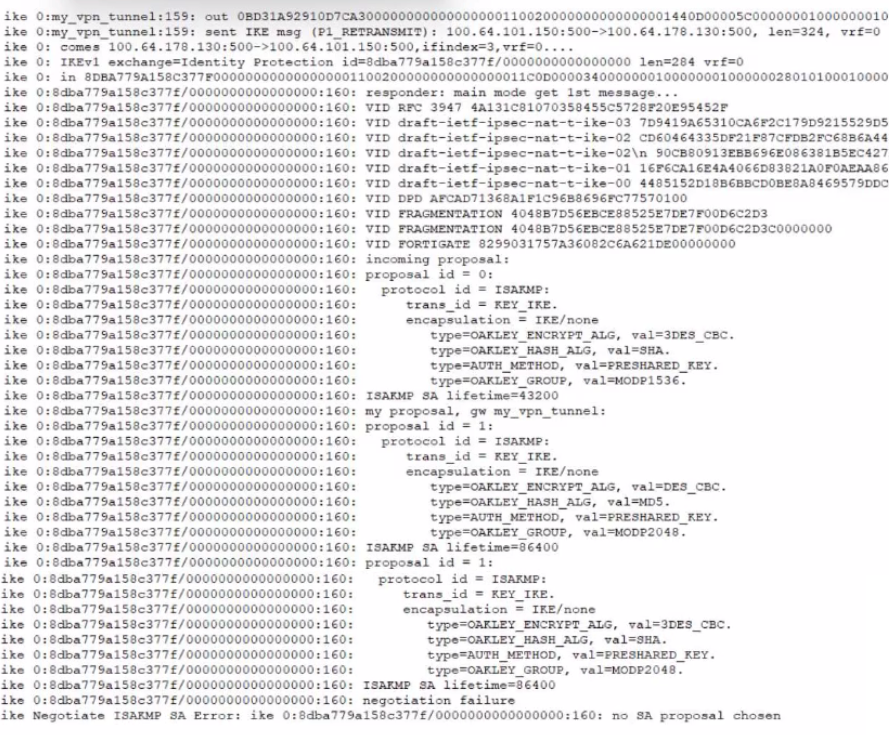
The VPN tunnel between headquarters and the branch office is not being established.
What is causing the problem?
Answer : A
 All Official Question Types