Page: 1
/ 14
Total 416 questions
GIAC Systems and Network Auditor GSNA Exam Questions
Question 1
John works as a Network Administrator for Perfect Solutions Inc. The company has a Linux-based network. John is working as a root user on the Linux operating system. He wants to forward all the kernel messages to the remote host having IP address 192.168.0.1. Which of the following changes will he perform in the syslog.conf file to accomplish the task?
Answer : A
kern.* @192.168.0.1
Answer D is incorrect. This entry will forward all the messages to the remote host having IP address 192.168.0.1.
Answer B is incorrect. This entry will not forward any message to the remote host having IP address 192.168.0.1.
Answer C is incorrect. This entry will not forward any kernel message to the remote host having IP address 192.168.0.1.
Question 2
In which of the following techniques does an attacker take network traffic coming towards a host at one port and forward it from that host to another host?
Answer : D
Port redirection is a technique by which an attacker takes network traffic coming towards a host at one port and redirects it from that host to
another host. For example, tools such as Fpipe and Datapipe are port redirection tools that accept connections at any specified port and
resend them to other specified ports on specified hosts. For example, the following command establishes a listener on port 25 on the test
system and then redirects the connection to port 80 on the target system using the source port of 25.
C .\>fpipe -l 25 -s 25 -r 80 IP_address
Answer C is incorrect. Firewalking is a technique for gathering information about a remote network protected by a firewall. This
technique can be used effectively to perform information gathering attacks. In this technique, an attacker sends a crafted packet with a TTL
value that is set to expire one hop past the firewall. If the firewall allows this crafted packet through, it forwards the packet to the next hop.
On the next hop, the packet expires and elicits an ICMP 'TTL expired in transit' message to the attacker. If the firewall does not allow the
traffic, there should be no response, or an ICMP 'administratively prohibited' message should be returned to the attacker.
A malicious attacker can use firewalking to determine the types of ports/protocols that can bypass the firewall. To use firewalking, the
attacker needs the IP address of the last known gateway before the firewall and the IP address of a host located behind the firewall. The
main drawback of this technique is that if an administrator blocks ICMP packets from leaving the network, it is ineffective.
Answer A is incorrect. Snooping is an activity of observing the content that appears on a computer monitor or watching what a user is
typing. Snooping also occurs by using software programs to remotely monitor activity on a computer or network device. Hackers or attackers
use snooping techniques and equipment such as keyloggers to monitor keystrokes, capture passwords and login information, and to intercept
e-mail and other private communications. Sometimes, organizations also snoop their employees legitimately to monitor their use of
organizations' computers and track Internet usage.
Answer B is incorrect. In UDP port scanning, a UDP packet is sent to each port of the target system. If the remote port is closed, the
server replies that the remote port is unreachable. If the remote Port is open, no such error is generated. Many firewalls block the TCP port
scanning, at that time the UDP port scanning may be useful. Certain IDS and firewalls can detect UDP port scanning easily.
Question 3
What will be the output of the following command?
echo $(date %M) > date.txt
Answer : D
The date command with the %M specifier prints the current time (Minutes). Since the output is redirected towards the date.txt file, the current
time (Minutes) will be printed in the date.txt file.
Question 4
This is a Windows-based tool that is used for the detection of wireless LANs using the IEEE 802.11a, 802.11b, and 802.11g standards. The main features of these tools are as follows:
It displays the signal strength of a wireless network, MAC address, SSID, channel details, etc.
It is commonly used for the following purposes:
a.War driving
b.Detecting unauthorized access pointsc.Detecting causes of interference on a WLAN
d.WEP ICV error trackinge.Making Graphs and Alarms on 802.11 Data, including Signal Strength
This tool is known as __________.
Answer : B
NetStumbler is a Windows-based tool that is used for the detection of wireless LANs using the IEEE 802.11a, 802.11b, and 802.11g
standards. The main features of NetStumbler are as follows:
It displays the signal strength of a wireless network, MAC address, SSID, channel details, etc.
It is commonly used for the following purposes:
a.War driving
b.Detecting unauthorized access points
c.Detecting causes of interference on a WLAN
d.WEP ICV error tracking
e.Making Graphs and Alarms on 802.11 Data, including Signal Strength
Answer D is incorrect. Kismet is an IEEE 802.11 layer2 wireless network detector, sniffer, and intrusion detection system.
Answer A is incorrect. THC-Scan is a war-dialing tool.
Answer C is incorrect. Absinthe is an automated SQL injection tool.
Question 5
You work as a Network Administrator for Tech Perfect Inc. You have a laptop running Windows Vista Ultimate. You want to configure Windows Defender on your laptop so that it does not take any action automatically whenever it scans malicious software. Rather, it should recommend the action and wait for your approval for taking any action. Which of the following actions will you take to accomplish the task?
Answer : D
According to the question, you want to prevent Windows Defender from taking any action automatically during the scanning of your laptop. In order to accomplish this, you will have to clear the Apply default actions to items detected during a scan check box in Defender Options.
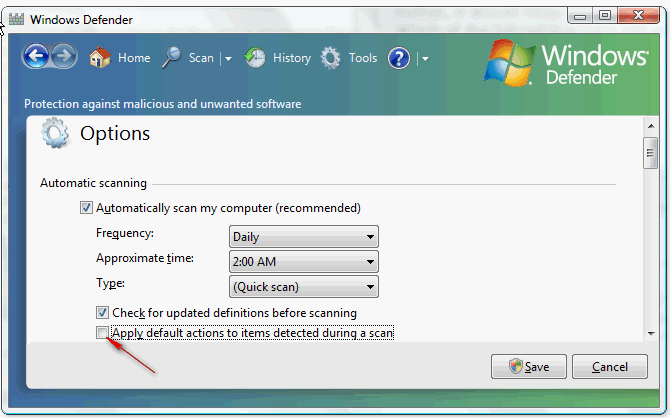
If you clear the Apply default actions to items detected during a scan check box, it will result in Windows Defender only recommending an
action to take for detected malicious software.
Question 6
You want to change the number of characters displaying on the screen while reading a txt file. However, you do not want to change the format of the txt file. Which of the following commands can be used to view (but not modify) the contents of the text file on the terminal screen at a time?
Answer : D
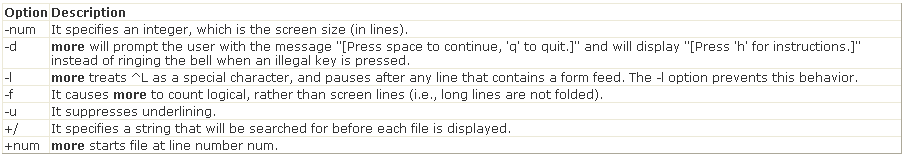
The more command is used to view (but not modify) the contents of a text file on the terminal screen at a time. The syntax of the more
command is as follows:
more [options] file_name
Where,
Answer A is incorrect. The concatenate (cat) command is used to display or print the contents of a file.
Syntax:
cat filename
For example, the following command will display the contents of the /var/log/dmesg file:
cat /var/log/dmesg
Note: The more command is used in conjunction with the cat command to prevent scrolling of the screen while displaying the contents of a file.
Answer C is incorrect. The less command is used to view (but not change) the contents of a text file, one screen at a time. It is similar
to the more command. However, it has the extended capability of allowing both forward and backward navigation through the file. Unlike
most Unix text editors/viewers, less does not need to read the entire file before starting; therefore, it has faster load times with large files.
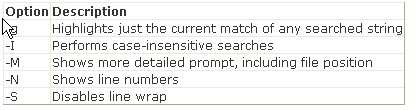
The command syntax of the less command is as follows:
less [options] file_name
Where,
Answer B is incorrect. The tail command is used to display the last few lines of a text file or piped data.
Question 7
You work as the Network Administrator for Perfect Solutions Inc. The company has a Linux-based network. You are a root user on the Red Hat
operating system. You want to keep an eye on the system log file /var/adm/messages. Which of the following commands should you use to
read the file in real time?
Answer : B
Using the -f option causes tail to continue to display the file in real time, showing added lines to the end of the file as they occur.
 All Official Question Types