Page: 1
/ 14
Total 57 questions
HashiCorp Certified: Vault Associate (002) Vault-Associate Exam Questions
Question 1
What are orphan tokens?
Answer : D
Orphan tokens are tokens that are root of their own token tree. This means that they do not have any parent token associated with them, and they do not expire when their parent token expires. Orphan tokens are useful for scenarios where you need a short-lived and independent token, such as for testing or debugging purposes. Orphan tokens can also be used to create temporary access tokens for applications or services that need to communicate with Vault without using a long-lived root token.Reference:Tokens | Vault | HashiCorp Developer,Vault cli: how to create orphan token with role - HashiCorp Discuss
Question 2
What can be used to limit the scope of a credential breach?
Answer : C
Using a short-lived dynamic secrets can help limit the scope of a credential breach by reducing the exposure time of the secrets. Dynamic secrets are generated on-demand by Vault and automatically revoked when they are no longer needed. This way, the credentials are not stored in plain text or in a static database, and they can be rotated frequently to prevent unauthorized access. Dynamic secrets also provide encryption as a service, which means that they perform cryptographic operations on data in-transit without storing any data. This adds an extra layer of security and reduces the risk of data leakage or tampering.Reference:Dynamic secrets | Vault | HashiCorp Developer,What are dynamic secrets and why do I need them? - HashiCorp
Question 3
You are performing a high number of authentications in a short amount of time. You're experiencing slow throughput for token generation. How would you solve this problem?
Answer : B
Batch tokens are a type of tokens that are not persisted in Vault's storage backend, but are encrypted blobs that carry enough information to perform Vault actions. Batch tokens are extremely lightweight and scalable, and can improve the throughput for token generation. Batch tokens are suitable for high-volume and ephemeral workloads, such as containers or serverless functions, that require short-lived and non-renewable tokens. Batch tokens can be created by using the -type=batch flag in the vault token create command, or by configuring the token_type parameter in the auth method's role or mount options. Batch tokens have some limitations compared to service tokens, such as the lack of renewal, revocation, listing, accessor, and cubbyhole features.Therefore, batch tokens should be used with caution and only when the trade-offs are acceptable.Reference: https://developer.hashicorp.com/vault/tutorials/tokens/batch-tokens1, https://developer.hashicorp.com/vault/docs/commands/token/create2, https://developer.hashicorp.com/vault/docs/concepts/tokens#token-types3
Question 4
A web application uses Vault's transit secrets engine to encrypt data in-transit. If an attacker intercepts the data in transit which of the following statements are true? Choose two correct answers.
Answer : B, D
A web application that uses Vault's transit secrets engine to encrypt data in-transit can benefit from the following security features:
Even if the attacker was able to access the raw data, they would only have encrypted bits (TLS in transit). This means that the attacker would need to obtain the encryption key from Vault in order to decrypt the data, which is protected by Vault's authentication and authorization mechanisms. The transit secrets engine does not store the data sent to it, so the attacker cannot access the data from Vault either.
The keys can be rotated and min_decryption_version moved forward to ensure this data cannot be decrypted. This means that the web application can periodically change the encryption key used to encrypt the data, and set a minimum decryption version for the key, which prevents older versions of the key from being used to decrypt the data. This way, even if the attacker somehow obtained an old version of the key, they would not be able to decrypt the data that was encrypted with a newer version of the key.
The other statements are not true, because:
You cannot rotate the encryption key so that the attacker won't be able to decrypt the data. Rotating the key alone does not prevent the attacker from decrypting the data, as they may still have access to the old version of the key that was used to encrypt the data. You need to also move the min_decryption_version forward to invalidate the old version of the key.
The Vault administrator would not need to seal the Vault server immediately. Sealing the Vault server would make it inaccessible to both the attacker and the legitimate users, and would require unsealing it with the unseal keys or the recovery keys. Sealing the Vault server is a last resort option in case of a severe compromise or emergency, and is not necessary in this scenario, as the attacker does not have access to the encryption key or the data in Vault.Reference:Transit - Secrets Engines | Vault | HashiCorp Developer,Encryption as a service: transit secrets engine | Vault | HashiCorp Developer
Question 5
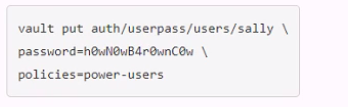
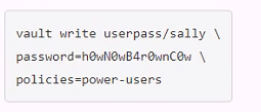
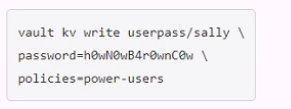
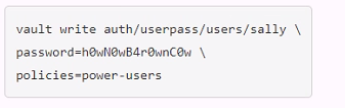
You are using the Vault userpass auth method mounted at auth/userpass. How do you create a new user named "sally" with password "h0wN0wB4r0wnC0w"? This new user will need the power-users policy.
A.
B.
C.
D.
Answer : D
To create a new user named ''sally'' with password ''h0wN0wB4r0wnC0w'' and the power-users policy, you would use the Vault userpass auth method mounted at auth/userpass. You would use the following command: ''vault write auth/userpass/users/sally password=h0wN0wB4r0wnC0w policies=power-users''. This command would create a new user named ''sally'' with the specified password and policy.Reference:
[Userpass Auth Method | Vault | HashiCorp Developer]
[Create Vault policies | Vault | HashiCorp Developer]
Question 6
The Vault encryption key is stored in Vault's backend storage.
Answer : B
The statement is false. The Vault encryption key is not stored in Vault's backend storage, but rather in Vault's memory. The Vault encryption key is the key that is used to encrypt and decrypt the data that is stored in Vault's backend storage, such as secrets, tokens, policies, etc. The Vault encryption key is derived from the master key, which is generated when Vault is initialized. The master key is split into unseal keys using Shamir's secret sharing algorithm, and the unseal keys are distributed to trusted operators. To start Vault, a quorum of unseal keys is required to reconstruct the master key and derive the encryption key. The encryption key is then kept in memory and used to protect the data in Vault's backend storage. The encryption key is never written to disk or exposed via the API.Reference:Seal/Unseal | Vault | HashiCorp Developer,Key Rotation | Vault | HashiCorp Developer
Question 7
Which of the following statements describe the CLI command below?
S vault login -method-1dap username-mitche11h
Answer : A
The CLI command vault login -method ldap username=mitchellh generates a token that is response wrapped. This means that the token contains a base64-encoded response wrapper, which is a JSON object that contains information about the token, such as its policies, metadata, and expiration time. The response wrapper is used to verify the authenticity and integrity of the token, and to prevent replay attacks. The response wrapper also allows Vault to automatically renew the token when it expires, or to revoke it if it is compromised. The -method ldap option specifies that the authentication method is LDAP, which requires a username and password to be provided. The username mitchellh is an example of an LDAP user name, and the password will be hidden when entered.Reference:Vault CLI Reference | Vault | HashiCorp Developer,Vault CLI Reference | Vault | HashiCorp Developer
 All Official Question Types