Page: 1
/ 14
Total 60 questions
HP Aruba Certified Network Security Expert Written HPE6-A84 Exam Questions
Question 1
Refer to the scenario.
This customer is enforcing 802.1X on AOS-CX switches to Aruba ClearPass Policy Manager (CPPM). The customer wants switches to download role settings from CPPM. The ''reception-domain'' role must have these settings:
--- Assigns clients to VLAN 14 on switch 1, VLAN 24 on switch 2, and so on.
--- Filters client traffic as follows:
--- Clients are permitted full access to 10.1.5.0/24 and the Internet
--- Clients are denied access to 10.1.0.0/16
The switch topology is shown here:

How should you configure the VLAN setting for the reception role?
Answer : A
According to the AOS-CX User Guide, one way to configure the VLAN setting for the reception role is to assign a consistent name to VLAN 14, 24, or 34 on each access layer switch and reference that name in the enforcement profile VLAN settings. This way, the switches can download the role settings from CPPM and apply the correct VLAN based on the name, rather than the ID. For example, the enforcement profile VLAN settings could be:

And the VLAN configuration on each switch could be:

Question 2
Refer to the scenario.
An organization wants the AOS-CX switch to trigger an alert if its RADIUS server (cp.acnsxtest.local) rejects an unusual number of client authentication requests per hour. After some discussions with other Aruba admins, you are still not sure how many rejections are usual or unusual. You expect that the value could be different on each switch.
You are helping the developer understand how to develop an NAE script for this use case.
You are helping the developer find the right URI for the monitor.
Refer to the exhibit.
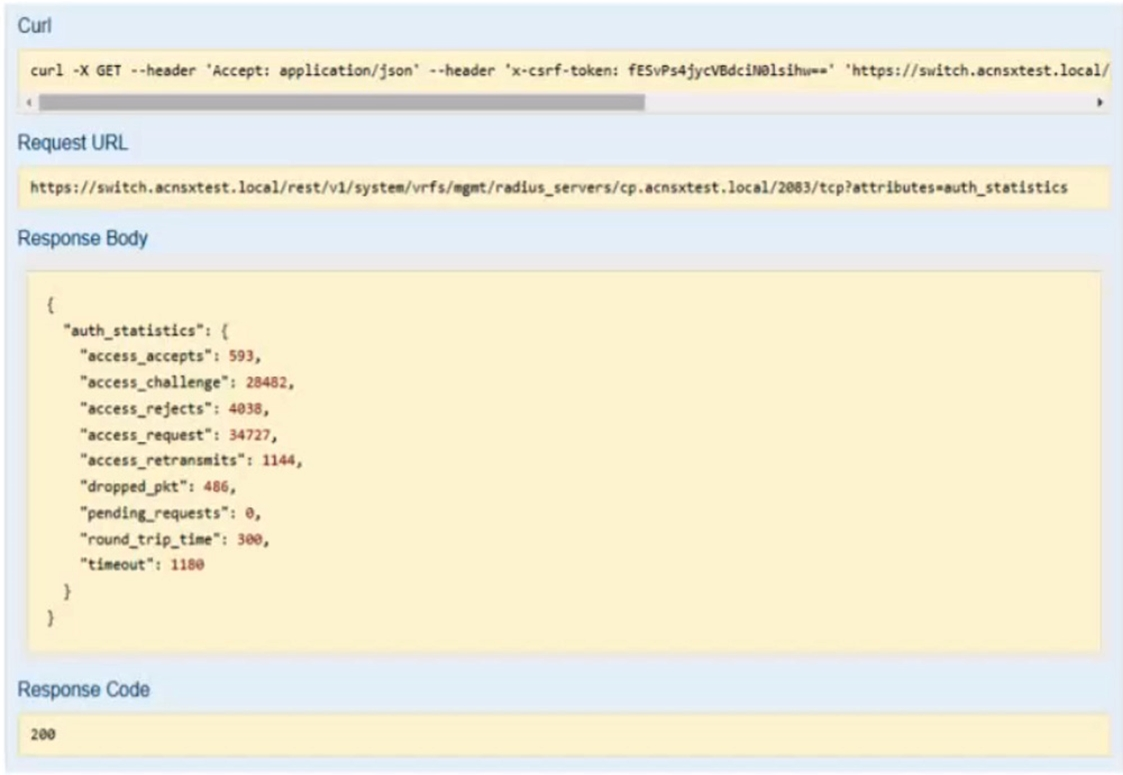
You have used the REST API reference interface to submit a test call. The results are shown in the exhibit.
Which URI should you give to the developer?
Answer : D
This is because this URI specifies the exact attribute that contains the number of access rejects from the RADIUS server, which is the information that the NAE script needs to monitor and trigger an alert.
A) /rest/v1/system/vrfs/mgmt/radius/servers/cp.acnsxtest.local/2083/tcp?attributes=authstatistics. This is not the correct URI because it returns the entire authstatistics object, which contains more information than the access rejects, such as access accepts, challenges, timeouts, etc. This might make the NAE script more complex and inefficient to parse and process the data.
B) /rest/v1/system/vrfs/mgmt/radius/servers/cp.acnsxtest.local/2083/tcp?attributes=authstatistics?attributes=access_rejects. This is not a valid URI because it has two question marks, which is a syntax error. The question mark is used to indicate the start of the query string, which can have one or more parameters separated by ampersands. The correct way to specify multiple attributes is to use a comma-separated list after the question mark, such as ?attributes=attr1,attr2,attr3.
C) /rest/v1/system/vrfs/mgmt/radius/_servers/cp.acnsxtest.local/2083/tcp. This is not a valid URI because it has an extra underscore before servers, which is a typo. The correct resource name is servers, not _servers. Moreover, this URI does not specify any attributes, which means it will return the default attributes of the RADIUS server object, such as name, port, protocol, etc., but not the authstatistics or access_rejects.
7of30
Question 3
Refer to the exhibit.
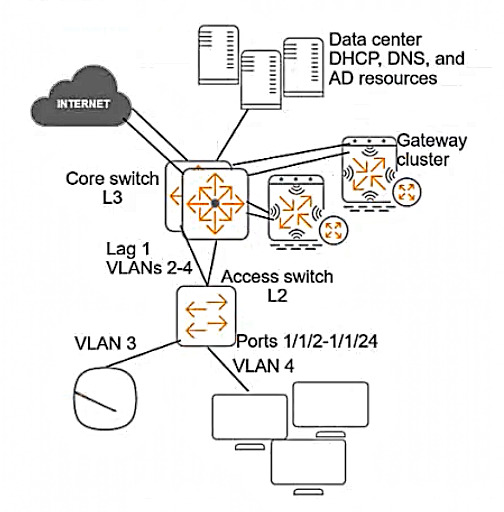
A customer requires protection against ARP poisoning in VLAN 4. Below are listed all settings for VLAN 4 and the VLAN 4 associated physical interfaces on the AOS-CX access layer switch:
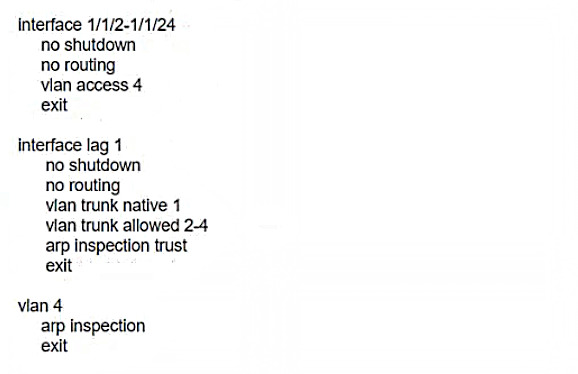
What is one issue with this configuration?
Answer : D
This is because ARP inspection is a security feature that validates ARP packets in a network and prevents ARP poisoning attacks12ARP inspection works by intercepting, logging, and discarding ARP packets with invalid IP-to-MAC address bindings1To enable ARP inspection, the switch needs to know which ports are trusted and which are untrusted. Trusted ports are those that connect to authorized DHCP servers or other network devices that are not vulnerable to ARP spoofing.Untrusted ports are those that connect to end hosts or devices that might send forged ARP packets13
In the exhibit, LAG 1 is configured as a trusted port for ARP inspection, which is correct because it connects to the core switch. However, the edge ports (1/1/1-1/1/24) are not configured as untrusted ports for ARP inspection, which is incorrect because they connect to end hosts that might be compromised by an attacker. By default, all ports are untrusted for ARP inspection, but this can be changed by using the commandip arp inspection truston the interface configuration mode3Therefore, to protect VLAN 4 against ARP poisoning, the edge ports should be configured as untrusted for ARP inspection by using the commandno ip arp inspection truston the interface configuration mode.This way, the switch will validate the ARP packets received on these ports against the DHCP snooping database or an ARP access-list and drop any invalid packets34
A) ARP proxy is not enabled on VLAN 4.This is not an issue because ARP proxy is an optional feature that allows the switch to respond to ARP requests on behalf of hosts in different subnets5It is not related to ARP poisoning or ARP inspection.
B) LAG 1 is configured as trusted for ARP inspection but should be untrusted. This is not an issue because LAG 1 connects to the core switch, which is a trusted device that does not send forged ARP packets.
C) DHCP snooping is not enabled on VLAN 4.This is not an issue because DHCP snooping is a separate feature that prevents rogue DHCP servers from offering IP addresses to clients6It is not directly related to ARP poisoning or ARP inspection, although it can provide information for ARP inspection validation if enabled
Question 4
Refer to the exhibit.

Aruba ClearPass Policy Manager (CPPM) is using the settings shown in the exhibit. You reference the tag shown in the exhibit in enforcement policies related to NASes of several types, including Aruba APs, Aruba gateways, and AOS-CX switches.
What should you do to ensure that clients are reclassified and receive the correct treatment based on the tag?
Answer : C
According to the ClearPass Policy Manager User Guide1, the tag shown in the exhibit is a Device Insight tag, which is used to classify and identify devices based on their behavior and characteristics. Device Insight tags can be used as conditions in enforcement policies to apply different actions or roles to devices based on their tags. However, in order to ensure that devices are reclassified and receive the correct treatment based on their tags, profiling must be enabled in each service that uses one of these enforcement profiles. Profiling is a feature that allows ClearPass to dynamically discover and profile devices on the network, and update their attributes and tags accordingly. Profiling also allows ClearPass to send RADIUS Change of Authorization (CoA) messages to the network access servers (NASes) that control the access of the devices, and instruct them to reauthenticate or terminate the sessions of the devices that have changed their tags. The profiling action must be set to the correct one for the NASes using that service, as different NASes may support different types of CoA messages. Therefore, option C is the correct answer.
Question 5
Refer to the scenario.
A customer has an Aruba ClearPass cluster. The customer has AOS-CX switches that implement 802.1X authentication to ClearPass Policy Manager (CPPM).
Switches are using local port-access policies.
The customer wants to start tunneling wired clients that pass user authentication only to an Aruba gateway cluster. The gateway cluster should assign these clients to the ''eth-internet" role. The gateway should also handle assigning clients to their VLAN, which is VLAN 20.
The plan for the enforcement policy and profiles is shown below:

The gateway cluster has two gateways with these IP addresses:
* Gateway 1
o VLAN 4085 (system IP) = 10.20.4.21
o VLAN 20 (users) = 10.20.20.1
o VLAN 4094 (WAN) = 198.51.100.14
* Gateway 2
o VLAN 4085 (system IP) = 10.20.4.22
o VLAN 20 (users) = 10.20.20.2
o VLAN 4094 (WAN) = 198.51.100.12
* VRRP on VLAN 20 = 10.20.20.254
The customer requires high availability for the tunnels between the switches and the gateway cluster. If one gateway falls, the other gateway should take over its tunnels. Also, the switch should be able to discover the gateway cluster regardless of whether one of the gateways is in the cluster.
You are setting up the UBT zone on an AOS-CX switch.
Which IP addresses should you define in the zone?
Answer : A
To configure user-based tunneling (UBT) on an AOS-CX switch, you need to specify the IP addresses of the mobility gateways that will receive the tunneled traffic from the switch1.The primary controller is the preferred gateway for the switch to establish a tunnel, and the backup controller is the alternative gateway in case the primary controller fails or becomes unreachable1.The IP addresses of the gateways should be their system IP addresses, which are used for inter-controller communication and cluster discovery2.
In this scenario, the customer has a gateway cluster with two gateways, each with a system IP address on VLAN 4085. Therefore, the switch should use these system IP addresses as the primary and backup controllers for UBT.The IP addresses of the gateways on VLAN 20 and VLAN 4094 are not relevant for UBT, as they are used for user traffic and WAN connectivity, respectively2.The VRRP IP address on VLAN 20 is also not applicable for UBT, as it is a virtual IP address that is not associated with any specific gateway3.
Therefore, the best option is to use 10.20.4.21 as the primary controller and 10.20.4.22 as the backup controller for UBT on the switch.This will ensure high availability and cluster discovery for the tunneled traffic from the switch to the gateway cluster12.
Question 6
Refer to the scenario.
A customer is using an AOS 10 architecture with Aruba APs and Aruba gateways (two per site). Admins have implemented auto-site clustering for gateways with the default gateway mode disabled. WLANs use tunneled mode to the gateways.
The WLAN security is WPA3-Enterprise with authentication to an Aruba ClearPass Policy Manager (CPPM) cluster VIP. RADIUS communications use RADIUS, not RadSec.
For which devices does CPPM require network device entries?
Answer : A
ClearPass Policy Manager (CPPM) requires network device entries for the devices that communicate with it using RADIUS or TACACS+ protocols. In this scenario, the gateways are the devices that act as RADIUS clients and send authentication requests to CPPM for the WLAN users. Therefore, CPPM needs to have network device entries for the gateways' actual IP addresses and the shared secrets that match the ones configured on the gateways.
Additionally, CPPM also requires network device entries for the gateways' dynamic authorization VRRP addresses, which are used for sending CoA messages to the gateways. CoA messages are used to change the attributes or status of a user session on the gateways without requiring re-authentication. For example, CPPM can use CoA to apply policies, roles, or bandwidth limits based on various conditions. To enable VRRP IP addresses for dynamic authorization, you need to set up gateway clusters manually and assign a VRRP VLAN and a VRRP IP address to each cluster. This way, CPPM can use the VRRP IP address as the NAS IP address for RADIUS communications and CoA messages. The VRRP IP address will remain the same even if the active gateway in the cluster changes due to a failover event, ensuring seamless operations.
Question 7
Refer to the scenario.
A customer has an Aruba ClearPass cluster. The customer has AOS-CX switches that implement 802.1X authentication to ClearPass Policy Manager (CPPM).
Switches are using local port-access policies.
The customer wants to start tunneling wired clients that pass user authentication only to an Aruba gateway cluster. The gateway cluster should assign these clients to the ''eth-internet" role. The gateway should also handle assigning clients to their VLAN, which is VLAN 20.
The plan for the enforcement policy and profiles is shown below:

The gateway cluster has two gateways with these IP addresses:
* Gateway 1
o VLAN 4085 (system IP) = 10.20.4.21
o VLAN 20 (users) = 10.20.20.1
o VLAN 4094 (WAN) = 198.51.100.14
* Gateway 2
o VLAN 4085 (system IP) = 10.20.4.22
o VLAN 20 (users) = 10.20.20.2
o VLAN 4094 (WAN) = 198.51.100.12
* VRRP on VLAN 20 = 10.20.20.254
The customer requires high availability for the tunnels between the switches and the gateway cluster. If one gateway falls, the other gateway should take over its tunnels. Also, the switch should be able to discover the gateway cluster regardless of whether one of the gateways is in the cluster.
Assume that you are using the ''myzone'' name for the UBT zone.
Which is a valid minimal configuration for the AOS-CX port-access roles?
Answer : B
The UBT solution requires that the edge ports on the switches are configured in VLAN trunk mode, not access mode. This is because the UBT solution uses a special VLAN (VLAN 4095 by default) to encapsulate the user traffic and tunnel it to the gateway. The edge ports need to allow this VLAN as well as any other VLANs that are used for management or control traffic.Therefore, the edge ports should be configured as VLAN trunk ports and allow the necessary VLANs1
1: Aruba Certified Network Technician (ACNT) | HPE Aruba Networking, section ''Get the Edge: An Introduction to Aruba Networking Solutions''
 All Official Question Types