Page: 1
/ 14
Total 220 questions
IAPP Certified Information Privacy Technologist CIPT Exam Questions
Question 1
SCENARIO
Tom looked forward to starting his new position with a U.S ---based automobile leasing company (New Company), now operating in 32 states. New Company was recently formed through the merger of two prominent players, one from the eastern region (East Company) and one from the western region (West Company). Tom, a Certified Information Privacy Technologist (CIPT), is New Company's first Information Privacy and Security Officer. He met today with Dick from East Company, and Harry, from West Company. Dick and Harry are veteran senior information privacy and security professionals at their respective companies, and continue to lead the east and west divisions of New Company. The purpose of the meeting was to conduct a SWOT (strengths/weaknesses/opportunities/threats) analysis for New Company. Their SWOT analysis conclusions are summarized below.
Dick was enthusiastic about an opportunity for the New Company to reduce costs and increase computing power and flexibility through cloud services. East Company had been contemplating moving to the cloud, but West Company already had a vendor that was providing it with software-as-a-service (SaaS). Dick was looking forward to extending this service to the eastern region. Harry noted that this was a threat as well, because West Company had to rely on the third party to protect its data.
Tom mentioned that neither of the legacy companies had sufficient data storage space to meet the projected growth of New Company, which he saw as a weakness. Tom stated that one of the team's first projects would be to construct a consolidated New Company data warehouse. Tom would personally lead this project and would be held accountable if information was modified during transmission to or during storage in the new data warehouse.
Tom, Dick and Harry agreed that employee network access could be considered both a strength and a weakness. East Company and West Company had strong performance records in this regard; both had robust network access controls that were working as designed. However, during a projected year-long transition period, New Company employees would need to be able to connect to a New Company network while retaining access to the East Company and West Company networks.
Which statement is correct about addressing New Company stakeholders' expectations for privacy?
Answer : C
The scenario presents the merger of two companies into New Company and outlines the discussions around privacy and security expectations. Addressing stakeholders' expectations for privacy is crucial in such a scenario.
Detailed Explanation:
Option A (Expect consumers to read privacy policy): While it is good practice to have a privacy policy, assuming that consumers will read and understand it may not be realistic. It is the company's responsibility to ensure that privacy practices are not just documented but also effectively implemented.
Option B (Manage stakeholder expectations for data not held by New Company): This option incorrectly assumes responsibility for data that is not within the control of New Company, which is impractical and not aligned with legal obligations.
Option C (Adhere to legal requirements): The best way to meet consumer expectations for privacy is to adhere to legal requirements. This ensures that the company complies with all relevant privacy laws and regulations, which is essential for protecting stakeholders' data and maintaining trust.
Option D (Commitment ends when data leaves New Company): This option misrepresents the ongoing responsibility that companies have over personal data even when shared with third parties. Proper contractual agreements and due diligence are necessary to ensure continued protection.
Adherence to legal requirements such as GDPR, CCPA, and other relevant privacy laws ensures that companies meet the minimum standards for data protection.
Regular audits and assessments to ensure compliance with privacy regulations.
The importance of transparency and accountability in handling personal data.
Conclusion: Adhering to legal requirements (Option C) is the most appropriate approach to meet consumer expectations for privacy, ensuring that New Company remains compliant with privacy laws and maintains stakeholders' trust.
Question 2
SCENARIO
Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed.
The table below indicates some of the personal information Clean-Q requires as part of its business operations:
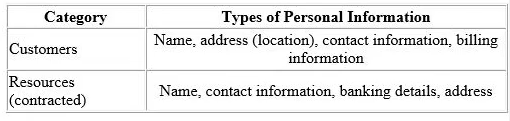
Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario.
With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings.
Ina business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and Cloud-Q's solution providers, presenting their proposed solutions and platforms.
The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information.
A customer facing web interface that enables customers to register, manage and submit cleaning service requests online.
A resource facing web interface that enables resources to apply and manage their assigned jobs.
An online payment facility for customers to pay for services.
Which question would you most likely ask to gain more insight about LeadOps and provide practical privacy recommendations?
Answer : C
To gain more insight about LeadOps and provide practical privacy recommendations, asking where LeadOps' operations and hosting services are located is essential.
Data Residency and Sovereignty: The physical location of data processing and storage facilities impacts compliance with data protection laws. Different countries have different regulations concerning data privacy and security.
Jurisdictional Issues: Knowing the location helps assess the legal jurisdiction governing the data. This includes understanding any potential requirements for data transfer, local laws, and the legal obligations LeadOps must comply with.
Cross-Border Data Transfers: If data is hosted in a different country, Clean-Q must ensure that adequate safeguards are in place for cross-border data transfers. This is particularly relevant under GDPR, which requires appropriate data transfer mechanisms like Standard Contractual Clauses (SCCs) or Binding Corporate Rules (BCRs).
Risk Assessment: The geopolitical stability and data protection framework of the hosting location can influence the security and privacy risks associated with using LeadOps.
IAPP Privacy Management, Information Privacy Technologist Certification Textbooks
GDPR Chapter V -- Transfers of Personal Data to Third Countries or International Organizations
NIST SP 800-37: Guide for Applying the Risk Management Framework to Federal Information Systems
Question 3
Which of the following is the best method to minimize tracking through the use of cookies?
Answer : D
Use 'private browsing' mode and delete checked files, clear cookies and cache once a day (A): While this can reduce tracking, it is not the most effective method for minimizing cookie tracking. Reference: IAPP CIPT Body of Knowledge.
Install a commercially available third-party application on top of the browser (B): This method may introduce additional risks and is not the most direct approach to managing cookies. Reference: IAPP CIPT Body of Knowledge.
Install and use a web browser that is advertised as 'built specifically to safeguard user privacy' (C): This can be effective, but it depends on the browser's capabilities and user settings. Reference: IAPP CIPT Body of Knowledge.
Manage settings in the browser to limit the use of cookies and remove them once the session completes (D): This is the most proactive and direct method to minimize tracking via cookies. Reference: IAPP CIPT Body of Knowledge.
Question 4
A key principle of an effective privacy policy is that it should be?
Answer : A
A key principle of an effective privacy policy is that it should be written in enough detail to cover the majority of likely scenarios. This ensures that the policy provides clear guidance on how personal data is to be handled, making it easier for employees to understand and follow, and for customers to know how their data is being used. According to the IAPP, privacy policies need to be sufficiently detailed to address the range of situations that the organization may encounter, which helps in maintaining compliance with privacy laws and regulations.
Question 5
A privacy engineer has been asked to review an online account login page. He finds there is no limitation on the number of invalid login attempts a user can make when logging into their online account.
What would be the best recommendation to minimize the potential privacy risk from this weakness?
Answer : A
Option A (Implement a CAPTCHA system): CAPTCHA (Completely Automated Public Turing test to tell Computers and Humans Apart) helps to prevent automated bots from attempting unlimited login attempts, reducing the risk of brute force attacks. It effectively adds a layer of security by ensuring that login attempts are made by humans, not automated scripts.
Option B (Server-side input validation checks): While important for overall security, input validation checks do not specifically address the issue of limiting invalid login attempts.
Option C (Enforce strong password and account credentials): Strong passwords and credentials are important but do not directly limit the number of invalid login attempts.
Option D (Implement strong TLS): Transport Layer Security (TLS) ensures encrypted communication but does not limit the number of login attempts.
OWASP (Open Web Application Security Project) guidelines on preventing brute force attacks.
NIST SP 800-63B Digital Identity Guidelines on authentication and brute force protection.
Conclusion: Implementing a CAPTCHA system (Option A) is the best recommendation to minimize the potential privacy risk from unlimited invalid login attempts, as it helps to distinguish between human and automated login attempts, reducing the risk of brute force attacks.
Question 6
Which of the following modes of interaction often target both people who personally know and are strangers to the attacker?
Answer : B
Phishing is a mode of interaction that can target both individuals who are known to the attacker and those who are strangers. Phishing attacks involve sending fraudulent messages (often via email) designed to trick recipients into revealing sensitive information or installing malware. This broad targeting method aims to reach as many people as possible, regardless of whether they have any prior relationship with the attacker. The IAPP documents highlight that phishing campaigns are often indiscriminate and wide-ranging, impacting both familiar and unfamiliar recipients.
Question 7
What risk is mitigated when routing video traffic through a company's application servers, rather than sending the video traffic directly from one user to another?
Answer : C
Option A: Phishing attacks are typically related to email or messaging security rather than direct video traffic.
Option B: While identity protection can be a factor, routing through company servers primarily obfuscates the user's IP address and other metadata, which reveals physical location rather than identity specifics.
Option C: Routing video traffic through a company's servers hides the users' IP addresses from each other, which prevents them from determining each other's physical location.
Option D: Stronger authentication methods are related to access control but not necessarily to the routing of video traffic.
IAPP CIPT Study Guide
Network security principles related to traffic routing
 All Official Question Types