Page: 1
/ 14
Total 98 questions
Juniper Security, Specialist JN0-335 Exam Questions
Question 1
You are deploying a new SRX Series device and you need to log denied traffic.
In this scenario, which two policy parameters are required to accomplish this task? (Choose two.)
Answer : B, C
you need to create a global firewall rulebase that matches RT_FLOW_SESSION_DENY events2.To do this, you need to specify two policy parameters:denyandsession-close3.
Question 2
Exhibit
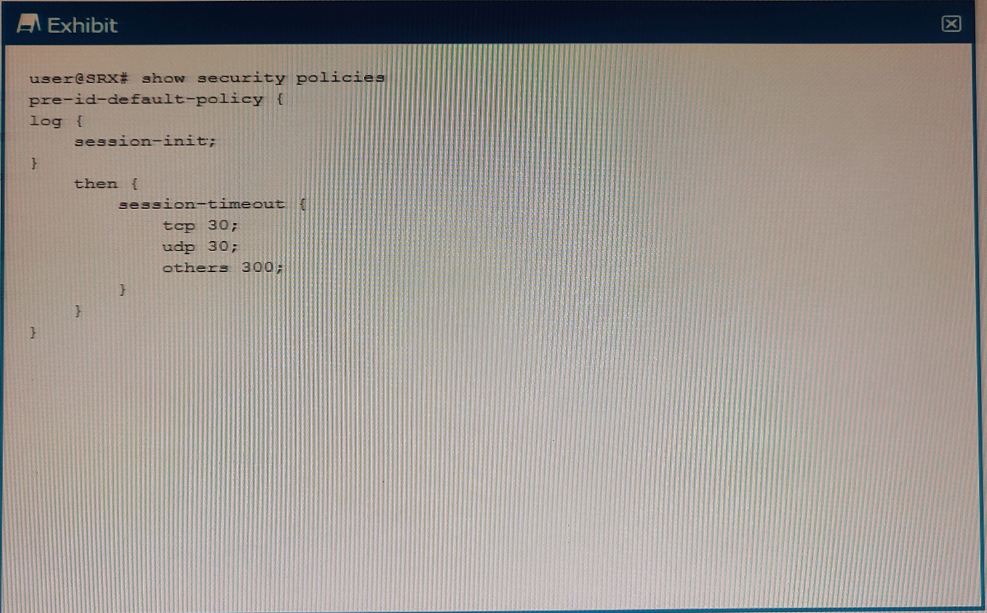
Which two statements are correct about the configuration shown in the exhibit? (Choose two.)
Answer : B, C
The configuration shown in the exhibit is for a Juniper SRX Series firewall. The session-init parameter is used to control how the firewall processes unknown traffic flows. With the session-init parameter set to 300, any traffic flows that the firewall does not recognize will be dropped after 300 milliseconds. Additionally, every session that enters the device, whether it is known or unknown, will generate an event, which can be used for logging and troubleshooting purposes. The session-lose parameter is used to control how the firewall handles established sessions that are terminated.
Question 3
What are two types of system logs that Junos generates? (Choose two.)
Answer : B, D
The two types of system logs that Junos generates are control plane logs and data plane logs. Control plane logs are generated by the Junos operating system and contain system-level events such as system startup and shutdown, configuration changes, and system alarms. Data plane logs are generated by the network protocol processes and contain messages about the status of the network and its components, such as routing, firewall, NAT, and IPS. SQL log files and system core dump files are not types of system logs generated by Junos.
Question 4
Regarding static attack object groups, which two statements are true? (Choose two.)
Answer : B, C
static attack object groups are predefined groups of attack objects that are included in Juniper's IPS signature database.These groups do not change automatically when Juniper updates the database2.
Question 5
Exhibit
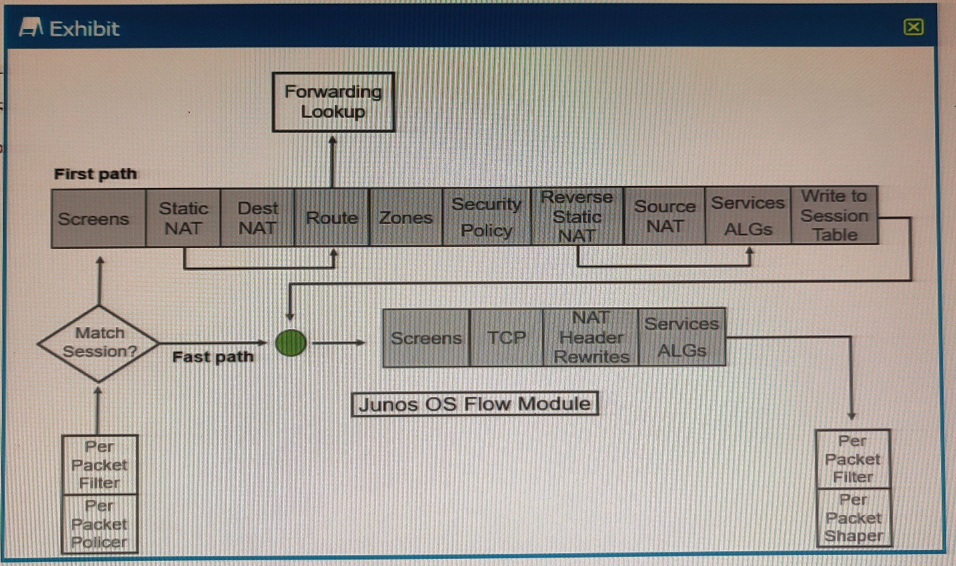
Referring to the SRX Series flow module diagram shown in the exhibit, where is application security processed?
Answer : B
Question 6
When a security policy is deleted, which statement is correct about the default behavior of active sessions allowed by that policy?
Answer : A
When a security policy is deleted, the active sessions allowed by the policy will be dropped. The default behavior is that all active sessions allowed by the policy will be terminated and the traffic will no longer be forwarded. There is no way to mark the active sessions as a legacy flow or to reevaluate them by the cached rules.
According to Juniper Networks Security, Specialist (JNCIS-SEC) Study Guide, when a security policy is deleted, the active sessions allowed by that policy will be dropped. This behavior is the default behavior of the device. There is no way to mark the active sessions as a legacy flow or to re-evaluate them against cached rules. The device will terminate the active sessions and will no longer forward traffic for those sessions.
Question 7
You are asked to determine how much traffic a popular gaming application is generating on your network.
Which action will you perform to accomplish this task?
Answer : D
AppTrack is a feature of Juniper Networks firewall solutions that allows administrators to track applications, users, and the amount of traffic generated by those applications on the network. AppTrack can be enabled on specific security zones of the network to monitor traffic on those zones. This feature can be used to determine how much traffic a popular gaming application is generating on the network. For more information, please refer to the Juniper Networks JNCIS-SEC Study Guide.
AppTrack is a feature of the Junos OS that provides visibility into the applications and users on your network. It tracks the usage of applications and provides detailed reports on the amount of traffic generated by each application. By enabling AppTrack on the proper security zones, you can determine how much traffic a popular gaming application is generating on your network.
 All Official Question Types