Page: 1
/ 14
Total 115 questions
Juniper Security, Professional JN0-636 JNCIP-SEC Exam Questions
Question 1
Exhibit
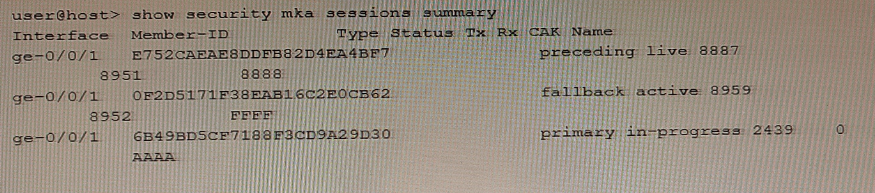
Referring to the exhibit, which two statements are true about the CAK status for the CAK named "FFFP"? (Choose two.)
Answer : A, D
The exhibit shows the output of the show security mka sessions summary command on an SRX Series device. This command displays the status of the MACsec Key Agreement (MKA) sessions on the device. In the output, we can see that there are two CAKs configured for the interface ge-0/0/1 - FFFF and EEEE. The CAK named FFFF has the type preceding and the status live. The CAK named EEEE has the type fallback and the status active.
The two statements that are true about the CAK status for the CAK named FFFF are:
CAK is not used for encryption and decryption of the MACsec session. This is because the CAK is only used for authentication and key exchange between the MACsec peers. The CAK is not used for encrypting or decrypting the MACsec traffic. The encryption and decryption of the MACsec session is done by the Secure Association Key (SAK), which is derived from the CAK using the MKA protocol.
SAK is not generated using this key. This is because the CAK named FFFF has the type preceding, which means that it is a legacy key that is used for backward compatibility with older MACsec devices. The preceding key is not used for generating the SAK, but only for authenticating the MACsec peers. The SAK is generated using the active key, which is the CAK named EEEE in this case.
Question 2
Exhibit
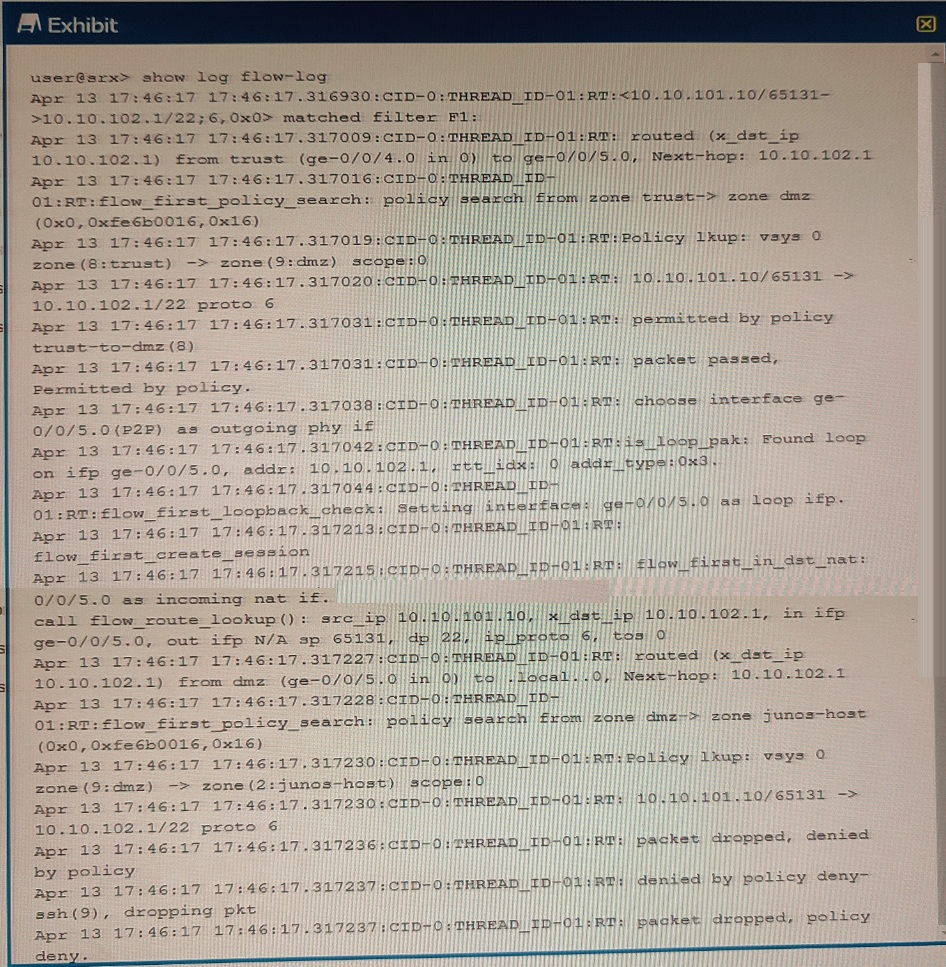
Referring to the exhibit, which three statements are true? (Choose three.)
Answer : A, C, D
According to the exhibit, which is a security flow trace on an SRX Series device, the following statements are true:
The packet's destination is to an interface on the SRX Series device.This is indicated by the linepacket dropped for self but not interested, which means that the packet is destined to the SRX device itself, but the device does not have the corresponding service configured in the host-inbound-traffic stanza for the interface1.
The packet originated within the Trust zone. This is indicated by the linezone name: Trust, which shows that the packet belongs to the Trust zone.The Trust zone is typically the zone where the internal network is connected to the SRX device2.
The packet is dropped before making an SSH connection. This is indicated by the lineflow_first_inline_processing: pak(0x4a9c0d0), which shows that the packet is the first packet in the session and is processed by the firewall.The packet is dropped because it does not match any security policy or host-inbound-traffic rule1. The packet is trying to make an SSH connection, which uses TCP port 22, as shown by the linesource port: 22.
The following statements are false:
The packet's destination is to a server in the DMZ zone. There is no indication of the DMZ zone in the trace output.The DMZ zone is typically the zone where the external servers are connected to the SRX device2.
The packet is allowed to make an SSH connection. The packet is not allowed to make an SSH connection, as explained above.
Question 3
To analyze and detect malware, Juniper ATP Cloud performs which two functions? (Choose two.)
Answer : A, C
Juniper ATP Cloud performs cache lookup to see if the file is seen already and known to be malicious and dynamic analysis to see what happens if you execute the file in a real environment.
Cache lookup is one of the functions that Juniper ATP Cloud performs to analyze and detect malware. Cache lookup is the first step in the pipeline approach that Juniper ATP Cloud uses to examine files. Cache lookup checks whether the file has been seen before and whether it has a stored verdict in the database. If the file is known to be malicious, the verdict is returned to the SRX Series Firewall and the file is dropped.If the file is not found in the cache, the analysis continues with the other techniques1.
Dynamic analysis is another function that Juniper ATP Cloud performs to analyze and detect malware. Dynamic analysis runs the file in a sandbox environment and observes its behavior and actions. Dynamic analysis can reveal the hidden or obfuscated functionality of malware, such as network connections, file modifications, registry changes, and process injections.Dynamic analysis can also detect zero-day threats and evasive malware that try to avoid static analysis1.
How is Malware Analyzed and Detected? | ATP Cloud | Juniper Networks
Question 4
Exhibit
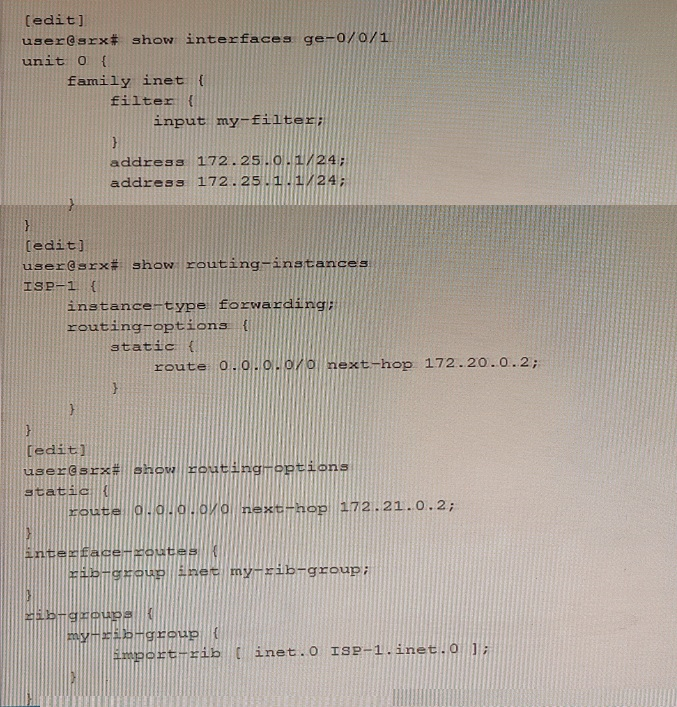
You are implementing filter-based forwarding to send traffic from the 172.25.0.0/24 network through ISP-1 while sending all other traffic through your connection to ISP-2. Your ge-0/0/1 interface connects to two networks, including the 172.25.0.0/24 network. You have implemented the configuration shown in the exhibit. The traffic from the 172.25.0.0/24 network is being forwarded as expected to 172.20.0.2, however traffic from the other network (172.25.1.0/24) is not being forwarded to the upstream 172.21.0.2 neighbor.
In this scenario, which action will solve this problem?
Answer : C
The exhibit shows the configuration of filter-based forwarding on an SRX Series device. Filter-based forwarding is a feature that allows the device to use firewall filters to direct traffic to different routing instances based on the match criteria. In this scenario, the device has two routing instances - ISP-1 and ISP-2 - and two firewall filters - FBF and FBF-ISP-1. The FBF filter is applied to the ge-0/0/1 interface as an input filter. The FBF filter has one term that matches the traffic from the 172.25.0.0/24 network and directs it to the ISP-1 routing instance. The ISP-1 routing instance has a static route to the next hop 172.20.0.2. The FBF-ISP-1 filter is applied to the ge-0/0/0 interface as an output filter. The FBF-ISP-1 filter has one term that matches the traffic to the 172.20.0.2 next hop and sets the forwarding class to expedited-forwarding.
The problem in this scenario is that the traffic from the other network (172.25.1.0/24) is not being forwarded to the upstream 172.21.0.2 neighbor. This is because the FBF filter does not have a term that accepts the traffic from the 172.25.1.0/24 network. The FBF filter only has one term that matches the traffic from the 172.25.0.0/24 network and directs it to the ISP-1 routing instance. The traffic from the 172.25.1.0/24 network does not match this term and is therefore discarded by the implicit deny action at the end of the filter. The traffic from the 172.25.1.0/24 network should be forwarded to the ISP-2 routing instance, which has a static default route to the next hop 172.21.0.2.
To solve this problem, you must add another term to the FBF filter to accept the traffic from the 172.25.1.0/24 network. This term should have the action accept, which means that the traffic will be forwarded according to the routing table of the master routing instance. The master routing instance has a static default route to the ISP-2 routing instance, which in turn has a static default route to the next hop 172.21.0.2. By adding this term, the traffic from the 172.25.1.0/24 network will be forwarded to the upstream 172.21.0.2 neighbor as expected.
The configuration of the new term in the FBF filter could look something like this:
[edit firewall family inet filter FBF] term 2 { from { source-address { 172.25.1.0/24; } } then { accept; } }
Question 5
Exhibit
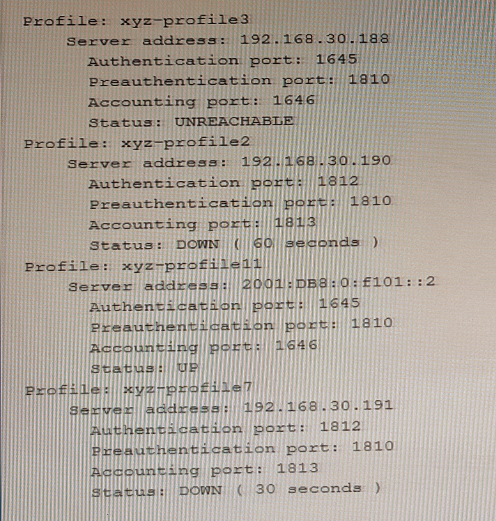
The show network-access aaa radius-servers command has been issued to solve authentication issues.
Referring to the exhibit, to which two authentication servers will the SRX Series device continue to send requests? (Choose TWO)
Answer : B, C
The SRX Series device will continue to send requests to authentication servers 192.168.30.190 and 192.168.30.191. This is because the exhibit shows the output of the show network-access aaa radius-servers command. This command displays the status of the RADIUS servers configured on the device. In the output, we can see that there are three RADIUS servers configured - 192.168.30.190, 192.168.30.191, and 2001:DB8:0:f101::2. However, the status of the third server is shown as ''DOWN''. This means that the device is not able to communicate with this server. Therefore, the device will continue to send requests to the other two servers - 192.168.30.190 and 192.168.30.191.Reference: Juniper Security, Professional (JNCIP-SEC) Reference Materials source and documents: https://www.juniper.net/documentation/en_US/junos/topics/reference/command-summary/show-network-access-aaa-radius-servers.html
Question 6
Exhibit
Referring to the exhibit, which two statements are true? (Choose two.)
Answer : A, C
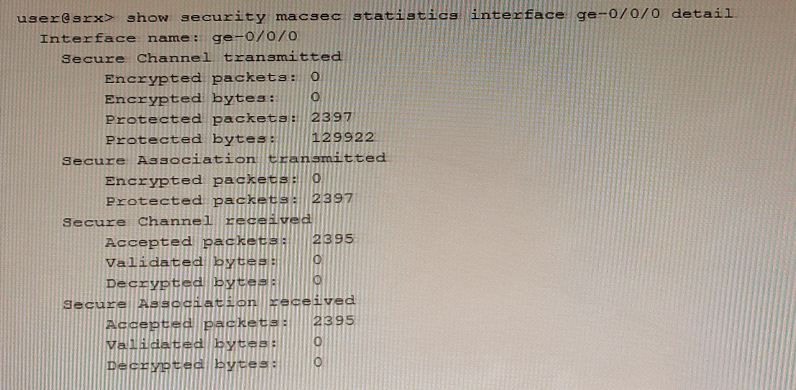
The exhibit shows the output of the show security macsec statistics interface ge-0/0/70 detail command on an SRX Series device. This command displays the statistics for the Media Access Control Security (MACsec) feature on the ge-0/0/70 interface. MACsec is a feature that provides point-to-point security on Ethernet links by using encryption and data integrity checks. MACsec uses two types of keys to secure the traffic: the Connectivity Association Key (CAK) and the Secure Association Key (SAK). The CAK is used for authentication and key exchange between the MACsec peers. The SAK is used for encryption and decryption of the MACsec traffic.
The two statements that are true based on the exhibit are:
The data that traverses the ge-0/0/70 interface is secured by a secure association key. This is because the exhibit shows that the interface has a Secure Channel (SC) and a Secure Association (SA) established. The SC is a logical connection between the MACsec peers that carries the encrypted traffic. The SA is a subset of the SC that contains the SAK and other parameters for encrypting and decrypting the traffic. The exhibit shows that the interface has encrypted and protected packets, which means that the traffic is secured by the SAK.
The data that traverses the ge-0/0/70 interface cannot be intercepted and read by anyone. This is because the exhibit shows that the interface has encryption enabled. The encryption option indicates whether the MACsec traffic is encrypted or not. If encryption is enabled, the traffic is encrypted by the SAK and cannot be viewed by anyone monitoring the link. If encryption is disabled, the traffic is only protected by the SAK and can be viewed by anyone monitoring the link.
Question 7
Refer to the exhibit,
which two potential violations will generate alarm ? (Choose Two)
Answer : A, D
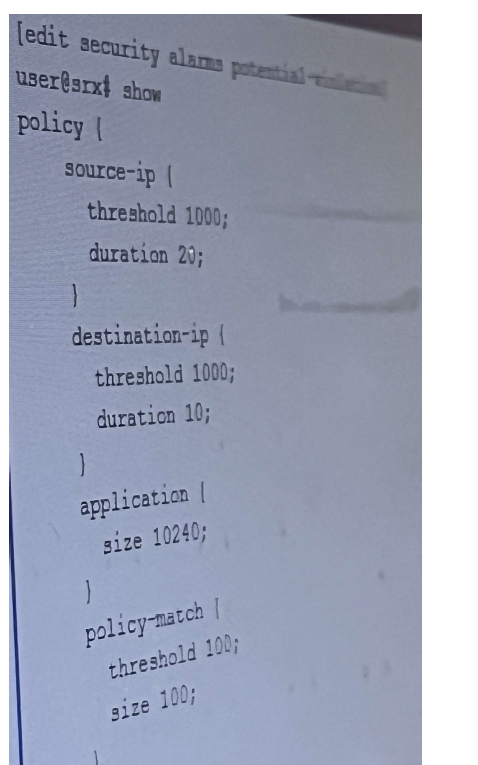
The exhibit shows a security policy configuration with a threshold of 1000 policy violations by a source network identifier and a threshold of 10 policy violations to an application within a specified period. If either of these thresholds are exceeded, an alarm will be generated. Therefore, the correct answer is A and D. The other options are incorrect because:
B) The ratio of policy violation traffic compared to accepted traffic is not a criterion for triggering an alarm. The security policy configuration does not specify any ratio or percentage of policy violation traffic that would cause an alarm.
C) The number of policy violation by a destination TCP port is also not a criterion for triggering an alarm. The security policy configuration does not specify any threshold or duration for policy violation by a destination TCP port.
policy (Security Alarms)
Monitoring Security Policy Violations
 All Official Question Types