Page: 1
/ 14
Total 115 questions
Juniper Security, Professional JN0-637 JNCIP-SEC Exam Questions
Question 1
A company has acquired a new branch office that has the same address space of one of its local networks, 192.168.100/24. The offices need to communicate with each other.
Which two NAT configurations will satisfy this requirement? (Choose two.)
Answer : A, D
The problem describes two offices needing to communicate, but both share the same IP address space, 192.168.100.0/24. To resolve this, NAT must be configured to translate the conflicting address spaces on each side. Here's how each of the configurations works:
Option A (Correct):
This source NAT rule translates the source address of traffic from Office B to Office A. By configuring source NAT, the source IP addresses from Office B (192.168.210.0/24) will be translated when communicating with Office A (192.168.200.0/24). This method ensures that there is no overlap in address space when packets are transmitted between the two offices.
Option D (Correct):
This is a source NAT rule configured on Office B, which translates the source addresses from Office A to prevent address conflicts. It ensures that when traffic is initiated from Office A to Office B, the overlapping address range (192.168.100.0/24) is translated.
Options B and C (Incorrect):
These options involve static NAT rules that map address ranges between the two offices, but they do not resolve the overlapping IP address space issue effectively. Static NAT is not the optimal solution in this scenario since the problem involves address space conflict, which requires translation of source addresses during communication.
Juniper Reference:
Juniper NAT Configuration Guide: Detailed instructions on how to configure source NAT and resolve address conflicts between networks.
Question 2
You are using ADVPN to deploy a hub-and-spoke VPN to connect your enterprise sites.
Which two statements are true in this scenario? (Choose two.)
Answer : C, D
Question 3
You have an initial setup of ADVPN with two spokes and a hub. A host at partner Spoke-1 is sending traffic to a host at partner Spoke-2.
In this scenario, which statement is true?
Answer : A
Question 4
Which two statements are true when setting up an SRX Series device to operate in mixed mode? (Choose two.)
Answer : C, D
In mixed mode, SRX devices can simultaneously handle Layer 2 switching and Layer 3 routing, but a reboot is required when configuring Layer 2 and Layer 3 interfaces to ensure the configuration takes effect. Layer 2 packets are switched within the defined bridge domain. Further guidance on SRX mixed mode can be found at Juniper Mixed Mode Documentation.
When an SRX Series device is configured in mixed mode, both Layer 2 switching and Layer 3 routing functionalities can be used on the same device. This enables the SRX to act as both a router and a switch for different interfaces. However, there are certain considerations:
Explanation of Answer C (Reboot Requirement):
After configuring the SRX to operate with at least one Layer 2 interface and one Layer 3 interface, the device needs to be rebooted. This is required to properly initialize the mixed mode configuration, as the SRX needs to switch between Layer 2 and Layer 3 processing modes.
Explanation of Answer D (Layer 2 Traffic Handling):
In mixed mode, traffic from Layer 2 interfaces is switched within the same bridge domain. A bridge domain defines a Layer 2 broadcast domain, and packets from Layer 2 interfaces are forwarded based on MAC addresses within that domain.
Juniper Security Reference:
Mixed Mode Overview: Juniper SRX devices can operate in mixed mode to handle both Layer 2 and Layer 3 traffic simultaneously. Reference: Juniper Mixed Mode Documentation.
Question 5
Referring to the exhibit,
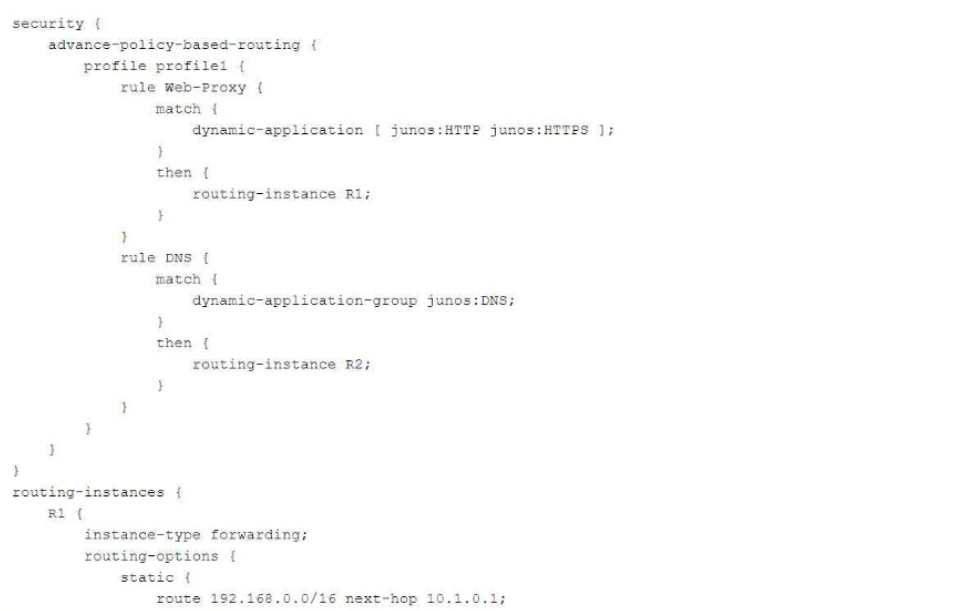
which statement about TLS 1.2 traffic is correct?
Answer : A
Question 6
Exhibit:
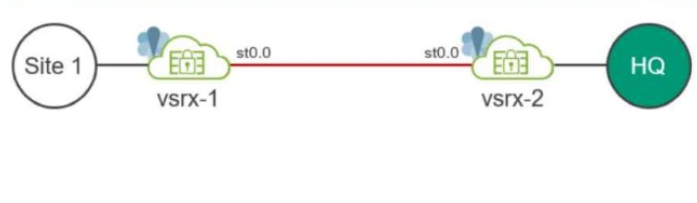
Your company uses SRX Series devices to establish an IPsec VPN that connects Site-1 and the HQ networks. You want VoIP traffic to receive priority over data traffic when it is forwarded across the VPN.
Which three actions should you perform in this scenario? (Choose three.)
Answer : B, C, E
Question 7
Exhibit:
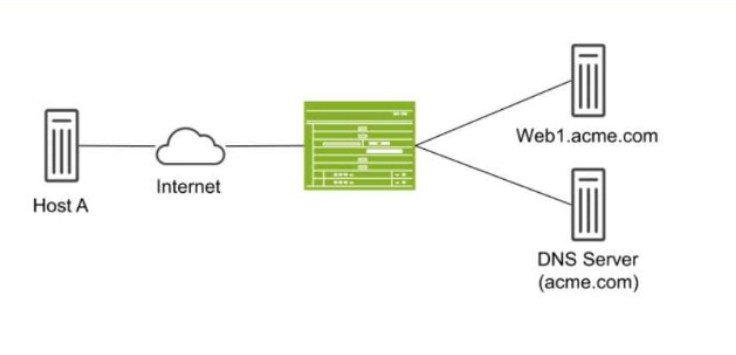
Host A shown in the exhibit is attempting to reach the Web1 webserver, but the connection is failing. Troubleshooting reveals that when Host A attempts to resolve the domain name of the server (web.acme.com), the request is resolved to the private address of the server rather than its public IP.
Which feature would you configure on the SRX Series device to solve this issue?
Answer : C
DNS doctoring modifies DNS responses for hosts behind NAT devices, allowing them to receive the correct public IP address for internal resources when queried from the public network. This prevents issues where private IPs are returned and are not reachable externally. For details, visit Juniper DNS Doctoring Documentation.
In this scenario, Host A is trying to resolve the domain name web.acme.com, but the DNS resolution returns the private IP address of the web server instead of its public IP. This is a common issue in networks where private addresses are used internally, but public addresses are required for external clients.
Explanation of Answer C (DNS Doctoring):
DNS doctoring is a feature that modifies DNS replies as they pass through the SRX device. In this case, DNS doctoring can be used to replace the private IP address returned in the DNS response with the correct public IP address for Host A. This allows external clients to reach internal resources without being aware of their private IP addresses.
Configuration Example:
bash
set security nat dns-doctoring from-zone untrust to-zone trust
Juniper Security Reference:
DNS Doctoring Overview: DNS doctoring is used to modify DNS responses so that external clients can access internal resources using public IP addresses. Reference: Juniper DNS Doctoring Documentation.
 All Official Question Types