Page: 1
/ 14
Total 65 questions
Juniper Data Center Professional JN0-683 Exam Questions
Question 1
You manage an IP fabric with an EVPN-VXLAN overlay. You have multiple tenants separated using multiple unique VRF instances. You want to determine the routing information that belongs in each routing instance's routing table.
In this scenario, which property is used for this purpose?
Answer : D, D
Understanding VRF and Routing Instances:
In an EVPN-VXLAN overlay network, multiple tenants are separated using unique VRF (Virtual Routing and Forwarding) instances. Each VRF instance maintains its own routing table, allowing for isolated routing domains within the same network infrastructure.
Role of Route Distinguisher:
Route Distinguisher (RD): The RD is a unique identifier used in MPLS and EVPN environments to distinguish routes belonging to different VRFs. The RD is prepended to the IP address in the route advertisement, ensuring that routes from different tenants remain unique even if they use the same IP address range.
Correct Property:
Question 2
You are asked to automatically provision new Juniper Networks devices in your network with minimal manual intervention Before you begin, which two statements are correct? (Choose two.)
Answer : A, D
Zero-Touch Provisioning (ZTP):
ZTP is a feature that allows for the automatic provisioning of devices with minimal manual intervention. It is widely used in large-scale deployments to quickly bring new devices online.
Key Requirements for ZTP:
A . DHCP Server: A DHCP server is crucial for ZTP as it provides the necessary information to new devices, such as the IP address, the location of the software image, and configuration files.
D . File Server: The file server is where the software image and configuration files are stored. The device downloads these files during the provisioning process.
Incorrect Options:
B . Syslog Server: While a syslog server is important for logging and monitoring, it is not a requirement for the initial provisioning process.
C . NTP Server: An NTP server is used for time synchronization, which is essential for accurate logging and operation but not specifically required for ZTP.
Data Center Reference:
ZTP simplifies the deployment process by automating the initial configuration steps, relying heavily on DHCP for communication and a file server for delivering the necessary configuration and software.
Question 3
Why is a designated forwarder required in a multihomed CE-to-PE VXLAN environment using EVPN signalling?
Answer : D
Understanding Multihomed CE-to-PE VXLAN Environment:
In a VXLAN environment using EVPN signaling, multiple PEs (Provider Edge devices) can be connected to the same CE (Customer Edge device). This setup is referred to as multihoming, where a CE device has multiple connections to the network to ensure redundancy and load balancing.
Role of the Designated Forwarder:
The designated forwarder (DF) is a mechanism used in EVPN to manage the forwarding of broadcast, unknown unicast, and multicast (BUM) traffic in a multihomed environment. The DF is selected to ensure that only one of the PEs forwards this type of traffic to the CE, preventing loops and unnecessary duplicate packets.
Avoiding Duplicate Packets:
Without a designated forwarder, all PEs connected to a multihomed CE could potentially forward the same packet to the CE, resulting in duplicate packets. This duplication can cause issues with packet processing on the CE, leading to inefficiencies and potential network problems.
Conclusion:
Option D: Correct---The designated forwarder is essential to prevent duplicate packets from being received on multihomed hosts, ensuring that only one PE forwards BUM traffic to the CE.
Question 4
Exhibit.
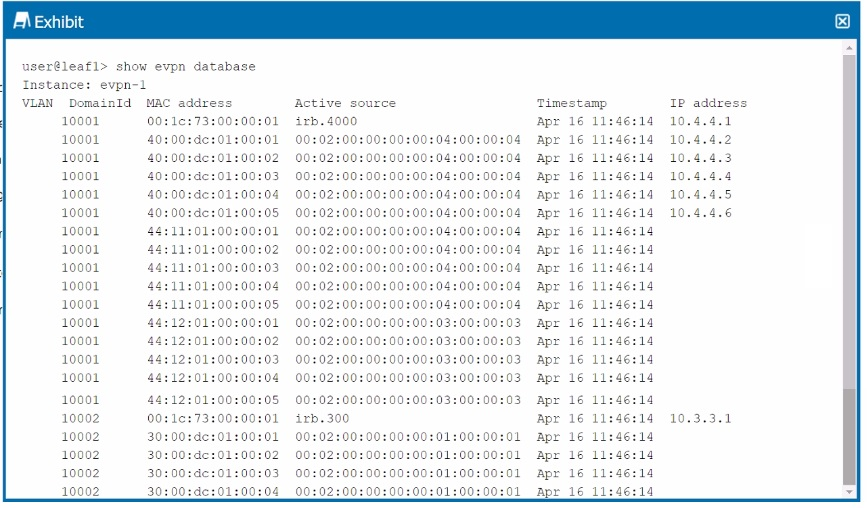
The exhibit shows the truncated output of the show evpn database command.
Given this output, which two statements are correct about the host with MAC address 40:00:dc:01:00:04? (Choose two.)
Answer : A, D
Understanding the Output:
The show evpn database command output shows the MAC address, VLAN, active source, timestamp, and IP address associated with various hosts in the EVPN instance.
Analysis of the MAC Address:
Option A: The MAC address 40:00:dc:01:00:04 is associated with the IP address 10.4.4.5, as indicated by the output in the IP address column. This confirms that this host has been assigned the IP 10.4.4.5.
Option D: The active source for the MAC address 40:00:dc:01:00:04 is listed as 00:02:00:00:00:04:00:04:00:00:04:00:04, which indicates that the host is connected via an ESI (Ethernet Segment Identifier) LAG (Link Aggregation Group). This setup is typically used in multi-homing scenarios to provide redundancy and load balancing across multiple physical links.
Conclusion:
Option A: Correct---The host with MAC 40:00:dc:01:00:04 is assigned IP 10.4.4.5.
Option D: Correct---The host is originating from an ESI LAG, as indicated by the active source value.
Question 5
Which three statements are correct about symmetric IRB routing with EVPN Type 2 routes? (Choose three.)
Answer : A, B, D
Symmetric IRB Routing with EVPN Type 2 Routes:
Symmetric Routing: In symmetric IRB (Integrated Routing and Bridging), routing occurs in both directions at the ingress and egress leaf nodes using the same routing logic. This is contrasted with asymmetric routing, where different routing logic is used depending on the direction of the traffic.
Required Components:
Option A: An L3 IRB interface is necessary for each VLAN that participates in routing, as it handles the Layer 3 processing for the VLAN.
Option B: MAC-VRF is required for symmetric routing to maintain a mapping of MAC addresses to the appropriate VRF, ensuring correct forwarding within the EVPN.
Option D: A transit VNI (Virtual Network Identifier) is required for each VRF to encapsulate the Layer 3 traffic as it traverses the network, allowing the IP traffic to be appropriately forwarded.
Conclusion:
Option A: Correct---Each local VLAN needs an IRB interface for L3 processing.
Option B: Correct---MAC-VRF is necessary for handling MAC address resolution in symmetric routing.
Option D: Correct---Transit VNIs are required for routing VRF-specific traffic across the network.
Options C and E are incorrect because:
C: Symmetric routing can work with various VLAN models, including single or multiple VLANs within an EVPN instance.
E: Symmetric routing is generally more efficient than asymmetric routing as it uses consistent routing logic in both directions.
Question 6
You are deploying a new network lo support your Al workloads on devices that support at least 400 Gbps Ethernet. There is no requirement for any Layer 2 VLANs in this network. Which network architecture would satisfy this requirement?
Answer : D
Requirements for AI Workloads:
The scenario requires a network that supports at least 400 Gbps Ethernet and does not require Layer 2 VLANs. This setup is well-suited for a pure Layer 3 network, which can efficiently route traffic between devices without the overhead or complexity of maintaining Layer 2 domains.
Choosing the Right Network Architecture:
Option D: An IP fabric using EBGP (External BGP) is ideal for this scenario. In a typical IP fabric, EBGP is used to handle routing between spine and leaf switches, creating a scalable and efficient network. Since there is no need for Layer 2 VLANs, the pure IP fabric design with EBGP provides a straightforward and effective solution.
Options A, B, and C involve more complex architectures (like VXLAN or EVPN), which are unnecessary when there's no requirement for Layer 2 overlays or VLANs.
Conclusion:
Option D: Correct---An IP fabric with EBGP is the most suitable and straightforward architecture for a network that needs to support high-speed AI workloads without Layer 2 VLANs.
Question 7
Exhibit.
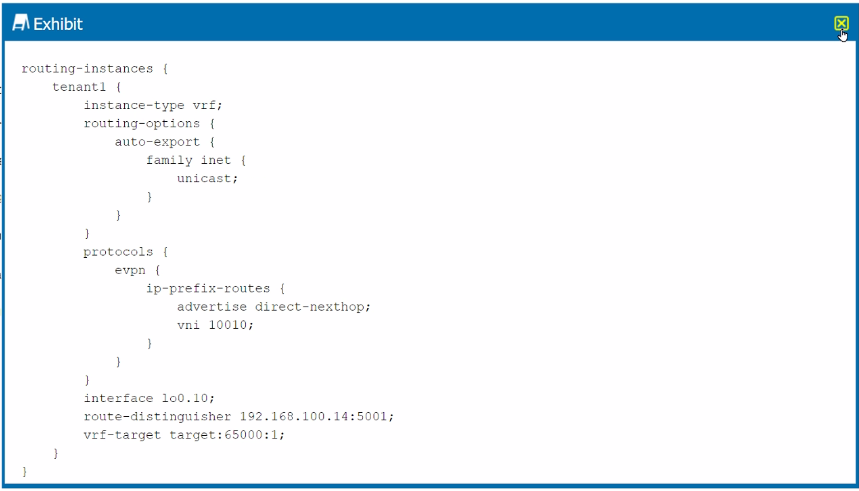
You want to enable the border leaf device to send Type 5 routes of local networks to the border leaf device in another data center. What must be changed to the configuration shown in the exhibit to satisfy this requirement?
Answer : A
In this scenario, you want the border leaf device to advertise Type 5 EVPN routes to another border leaf in a different data center. Type 5 routes in EVPN are used to advertise IP prefixes, which means that for proper route advertisement, you need to configure the correct settings within the evpn hierarchy.
Step-by-Step Analysis:
Understanding EVPN Type 5 Routes:
EVPN Type 5 routes are used to advertise IP prefixes across EVPN instances, which allow different data centers or networks to exchange routing information effectively.
VRF Target Setting:
The vrf-target configuration is crucial because it defines the export and import policies for the VRF within the EVPN instance. For EVPN Type 5 routes to be advertised to other border leaf devices, the vrf-target needs to be correctly configured under the evpn hierarchy, not just within the routing instance.
Command to solve this:
move vrf-target target:65000:1 to evpn
Other Options:
Option B: Adding a VLAN configuration would not address the requirement to advertise Type 5 routes.
Option C: Adding VXLAN encapsulation may be necessary for other scenarios but does not directly address the Type 5 route advertisement.
Option D: Changing the route-distinguisher will differentiate routes but does not impact the advertisement of Type 5 routes to other data centers.
By moving the vrf-target to the evpn hierarchy, you enable the proper route advertisement, ensuring that the Type 5 routes for local networks are shared with other data center border leaf devices. This is aligned with best practices for multi-data center EVPN implementations, which emphasize the correct placement of routing policies within the EVPN configuration.
 All Official Question Types