Page: 1
/ 14
Total 223 questions
Microsoft Administering Information Security in Microsoft 365 SC-401 Exam Questions
Question 1
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant and 500 computers that run Windows 11. The computers are onboarded to Microsoft Purview.
You discover that a third-party application named Tailspin_scanner.exe accessed protected sensitive information on multiple computers. Tailspin_scanner.exe is installed locally on the computers.
You need to block Tailspin_scanner.exe from accessing sensitive documents without preventing the application from accessing other documents.
Solution: From the Microsoft 365 Endpoint data loss prevention (Endpoint DLP) settings, you add a folder path to the file path exclusions.
Does this meet the goal?
Answer : B
Adding a folder path to the file path exclusions in Microsoft 365 Endpoint DLP does not prevent Tailspin_scanner.exe from accessing protected sensitive information. Instead, it would exclude those files from DLP protection, which is not the intended outcome.
To block Tailspin_scanner.exe from accessing sensitive documents while allowing it to access other files, the correct solution is to use Microsoft Purview Endpoint Data Loss Prevention (Endpoint DLP) and add Tailspin_scanner.exe to the Restricted Apps list.
Endpoint DLP allows you to block specific applications from accessing sensitive files while keeping general access available. Restricted Apps List in Endpoint DLP ensures that Tailspin_scanner.exe cannot open, copy, or process protected documents, but it can still function normally for non-sensitive content.
Question 2
You have a Microsoft 565 subscription that contains 100 users and a Microsoft 365 group named Group1. All users have Windows 11 devices and use Microsoft SharePoint Online and Exchange Online. A sensitivity label named Label! is published as the default label for Group1. You add two sublabels named Sublabel1 and Sublabel2 lo Label1. You need to ensure that the settings in Sublabel 1 are applied by default to Group 1. What should you do?
Answer : C
Question 3
You are creating a custom trainable classifier to Identify organizational product codes referenced in Microsoft 36S content. You identify 300 files to use as seed content When? should you store the seed content?
Answer : D
Question 4
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site! and the data loss prevention (DLP) policies shown in the following table.
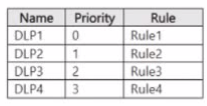
The DLP rules are configured as shown In the following table.
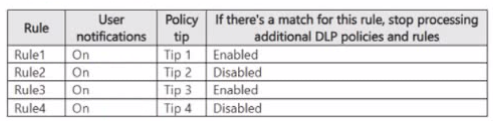
All the policies are assigned to Site1.
You need to ensure that if a user uploads a document to Site1 that matches all the rules, the user will be shown the Tip 2 policy tip. What should you do?
Answer : B
Question 5
You implement Microsoft 36S Endpoint data loss pi event ion (Endpoint DIP).
You have computers that run Windows 11 and have Microsoft 365 Apps instated The computers are joined to a Microsoft Entra tenant.
You need to ensure that Endpoint DIP policies can protect content on the computers.
Solution: You onboard the computers to Microsoft Defender for Endpoint Does this meet the goal?
Answer : A
Question 6
You have a Microsoft 365 subscription.
You create a new trainable classifier.
You need to train the classifier.
Which source can you use to train the classifier?
Answer : C
Question 7
You have a Microsoft 36S ES subscription that contains a Windows 11 device named Device 1 and three users named User 1. User2. and User3.
You plan to deploy Azure Information Protection (AIP) and the Microsoft Purview Information Protection client to Device 1.
You need to ensure that the users can perform the following actions on Device1 as part of the planned deployment
* User 1 will test the functionality of the client.
* User2 will install and configure the Microsoft Rights Management connector.
* User3 will be configured as the service account for the information protection scanner.
The solution must maximize the security of the sign-in process for the users What should you do?
Answer : B
 All Official Question Types