Page: 1
/ 14
Total 129 questions
Netskope Certified Cloud Security Administrator Exam NSK101 NCCSA Exam Questions
Question 1
A customer changes CCI scoring from the default objective score to another score. In this scenario, what would be a valid reason for making this change?
Answer : B
The CCI scoring is a way to measure the security posture of cloud applications based on a set of criteria and weights. The default objective score is calculated by Netskope using industry best practices and standards. However, customers can change the CCI scoring to suit their own business needs and risk appetite. For example, a customer may want to place a higher business risk weight on vendors that claim ownership of their data, as this may affect their data sovereignty and privacy rights. Changing the CCI scoring for this reason would be valid, as it reflects the customer's own security requirements and preferences. Changing the CCI scoring for other reasons, such as discovering a new SaaS application, punishing an application vendor, or using an application under research, would not be valid, as they do not align with the purpose and methodology of the CCI scoring.Reference:Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Course, Module 7: Cloud Confidence Index (CCI), Lesson 1: CCI Overview and Lesson 2: CCI Scoring.
Question 2
Click the Exhibit button.
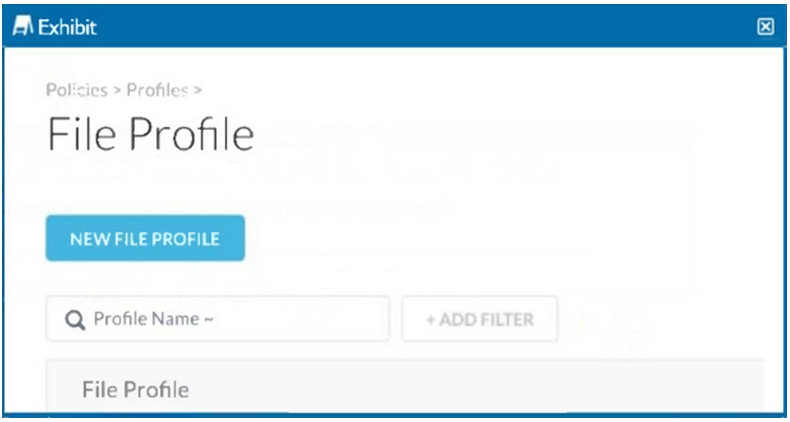
What are two use cases where the parameter shown in the exhibit is required? (Choose two.)
Answer : A, C
The parameter shown in the exhibit (File Profile) is crucial in policies where file type, size, and other attributes need to be specified. Here are two use cases where this parameter is required:
When you create a policy to prevent file transfer between a sanctioned Google Drive and personal Google Drive:
Implementation: Create a new File Profile with the desired file types and apply this profile in the policy that governs the data transfer rules between sanctioned and personal Google Drive instances.
When you create a policy to prevent binary files larger than 5 MB that are shared publicly on a sanctioned OneDrive:
Implementation: Define a File Profile that specifies binary files and sets a size limit (e.g., 5 MB). Apply this profile in the policy to prevent such files from being shared publicly.
REST API v2 Overview - Netskope Knowledge Portal
Using the REST API v2 dataexport Iterator Endpoints - Netskope Knowledge Portal
Using the REST API v2 UCI Impact Endpoints - Netskope Knowledge Portal
netskopesdk * PyPI
Netskope Rest APIv2(OAS 3.1) - Postman Collection
Question 3
Which three statements are correct about Netskope's NewEdge Security Cloud Network Infrastructure? (Choose three.)
Answer : B, C, D
Netskope's NewEdge Security Cloud Network Infrastructure is a global network that powers the Netskope Security Cloud, providing real-time inline and out-of-band API-driven services for cloud and web security. Three statements that are correct about Netskope's NewEdge Security Cloud Network Infrastructure are:
It includes direct peering with Microsoft and Google in every data center. This means that Netskope has established high-speed, low-latency connections with these major cloud service providers, ensuring optimal performance and user experience for their customers. Direct peering also reduces the risk of network congestion, packet loss, or routing issues that may affect the quality of service.
It is a private security cloud network that is massively over provisioned, highly elastic, and built for scale. This means that Netskope owns and operates its own network infrastructure, without relying on third-party providers or public cloud platforms. Netskope has invested over $150 million to build the world's largest and fastest security private cloud, with data centers in more than 65 regions and growing. Netskope can dynamically scale its network capacity and resources to meet the growing demand and traffic volume of its customers, without compromising on security or performance.
It delivers a single, unified network with no surcharges or reliance on public cloud infrastructure or virtual PoPs. This means that Netskope provides a consistent and transparent network service to its customers, regardless of their location or device. Netskope does not charge any additional fees or hidden costs for accessing its network services, unlike some other providers that may impose surcharges based on geography or bandwidth usage. Netskope also does not use virtual points of presence (PoPs) that are hosted on public cloud platforms, which may introduce latency, complexity, or security risks.
Question 4
Which two statements are correct about DLP Incidents in the Netskope platform? (Choose two.)
Answer : B, D
Two statements that are correct about DLP Incidents in the Netskope platform are: An incident can have one or more DLP violations and an incident can be associated to one or more DLP rules. A DLP violation occurs when a file or object matches a DLP rule used in a DLP profile. A DLP rule defines the criteria for detecting sensitive data, such as keywords, regular expressions, fingerprints, machine learning classifiers, etc. A DLP profile is a collection of DLP rules that can be applied to a policy. An incident is a record of a file or object that triggered a DLP policy violation. An incident can have multiple violations if the file or object matches multiple DLP rules from different profiles. An incident can also be associated to multiple DLP rules if the file or object matches more than one rule from the same profile.Reference:About DLPDLP Profiles
Question 5
You need to locate events for specific activities such as "edit" or "login successful" in a cloud application.
In which SkopeIT Events & Alerts page would this information be found?
Answer : C
The Application Events page in the SkopeIT Events & Alerts section is where you can find logs and events related to specific activities within cloud applications, such as 'edit' or 'login successful'. This section provides a detailed audit trail of user activities and application usage, which is essential for monitoring, security, and compliance purposes.
This answer is validated by the event categorization provided in the Netskope documentation, where application-specific events are logged under the Application Events section for easier tracking and analysis.
========
REST API v2 Overview - Netskope Knowledge Portal
Using the REST API v2 UCI Impact Endpoints - Netskope Knowledge Portal
Postman Collection for Netskope API
Question 6
You need to block all users from uploading data files into risky collaboration applications. Which element must you configure within Netskope's CASB to accomplish this task?
Answer : B
A real-time policy is a type of policy in Netskope's CASB that allows you to control the actions that users can perform on cloud applications in real time. You can use a real-time policy to block all users from uploading data files into risky collaboration applications by specifying the following elements: the application category (such as Collaboration), the activity (such as Upload), the file type (such as Data), the risk level (such as High or Very High), and the action (such as Block). A DLP rule, a DLP profile, and a block notification are not sufficient to accomplish this task, as they are either sub-components or outcomes of a real-time policy.Reference:Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Course, Module 5: Real-Time Policies, Lesson 1: Real-Time Policy Overview and Lesson 2: Real-Time Policy Configuration.
Question 7
You determine that a business application uses non-standard HTTPS ports. You want to steer all HTTPS traffic for this application and have visibility and control over user activities.
Which action will allow you to accomplish this task?
Answer : C
Identify Non-standard HTTPS Ports:
Determine the specific non-standard HTTPS ports used by the business application.
Create a Steering Exception:
Navigate to the Netskope admin console.
Go to the steering configuration section and create a new steering exception.
Specify the domain of the business application and include the non-standard HTTPS ports.
This exception will ensure that traffic to this application is steered correctly for inspection and control.
Configure Non-standard Ports in the Steering Configuration:
Go to the steering configuration settings.
Add the identified non-standard HTTPS ports to ensure that all traffic using these ports is captured and inspected.
This ensures comprehensive visibility and control over the user activities on the application.
Reference:
For more details on steering configurations and managing exceptions, refer to the Netskope documentation on steering traffic and configuring non-standard ports.
 All Official Question Types