Page: 1
/ 14
Total 60 questions
Netskope Certified Cloud Security Architect NSK300 Exam Questions
Question 1
You successfully configured Advanced Analytics to identify policy violation trends Upon further investigation, you notice that the activity is NULL. Why is this happening in this scenario?
Answer : D
The reason for the activity being NULL in this scenario is likely because a user accessed a static Web page. In Netskope's Advanced Analytics, when the activity is reported as NULL, it often indicates that there was no dynamic interaction or transaction to record, which is typical when a static web page is accessed1. Static web pages do not generate the kind of events or activities that are tracked by policies, hence they appear as NULL in the activity field.
Question 2
You deployed IPsec tunnels to steer on-premises traffic to Netskope. You are now experiencing problems with an application that had previously been working. In an attempt to solve the issue, you create a Steering Exception in the Netskope tenant tor that application: however, the problems are still occurring
Which statement is correct in this scenario?
Answer : C
In the scenario where you have deployed IPsec tunnels to steer on-premises traffic to Netskope and are experiencing issues with an application, the correct statement is C: Steering bypasses for IPsec tunnels must be applied at your edge network device. This means that to effectively bypass the steering for a specific application, the configuration must be done on the network device that is establishing the IPsec tunnel, such as a firewall or router. This device controls the traffic before it enters the tunnel, so applying the bypass there ensures that the application's traffic does not get directed through the tunnel and can reach its destination directly.
Question 3
You are asked to create a customized restricted administrator role in your Netskope tenant for a newly hired employee. Which two statements are correct in this scenario? (Choose two.)
Answer : A, C
Admin Role and File Content Viewing: By default, an admin role doesnotprevent admins from downloading and viewing file content. Admins have access to view and download file content unless specific restrictions are applied.
Role Privileges Default to Read Only: All role privileges in Netskope default toRead Onlyfor all functional areas. This means that admins can view information but cannot make changes unless explicitly granted additional permissions.
Obfuscation: Obfuscation can be applied to specific functional areas, but it is not a default behavior for all areas.Reference:
Netskope Security Cloud Introductory Online Technical Training
Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Training
Question 4
You have an NG-SWG customer that currently steers all Web traffic to Netskope using the Netskope Client. They have identified one new native application on Windows devices that is a certificate-pinned application. Users are not able to access the application due to certificate pinning. The customer wants to configure the Netskope Client so that the traffic from the application is steered to Netskope and the application works as expected.
Which two methods would satisfy the requirements? (Choose two.)
Answer : B, C
To address the issue of a certificate-pinned application not being accessible due to certificate pinning, while still steering the traffic to Netskope, the two methods that would satisfy the requirements are:
B: Configure the SSL Do Not Decrypt policy to not decrypt traffic for domains used by the native application. This ensures that the SSL traffic for the specified domains is not decrypted, thus avoiding issues with certificate pinning.
C: Configure domain exceptions in the steering configuration for the domains used by the native application. By setting domain exceptions, traffic to these domains will bypass SSL decryption, allowing the certificate-pinned application to function as expected1.
These methods are in line with Netskope's capabilities for handling certificate-pinned applications, which often require bypassing decryption to prevent breaking the application's functionality due to its security features1.
Question 5
Review the exhibit.
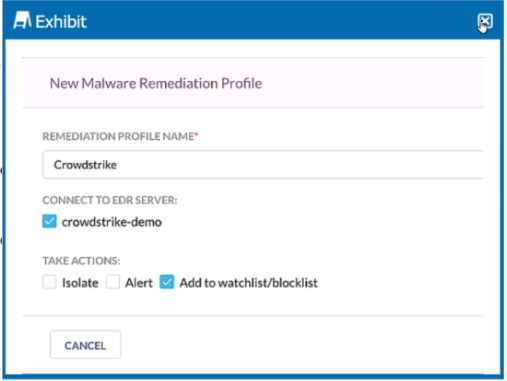
You are asked to integrate Netskope with Crowdstrike EDR. You added the Remediation profile shown in the exhibit.
Which action will this remediation profile take?
Answer : A
The remediation profile shown in the exhibit will take the action of isolating the endpoint. This is indicated by the ''Isolate'' option being checked under ''TAKE ACTIONS'' in the configuration settings. When this option is selected, the remediation profile is configured to isolate the endpoint upon detection of a threat, which is a common response to contain a potential security breach and prevent further spread of malware within the network1.
Question 6
Review the exhibit.
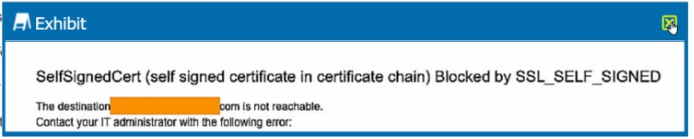
You are the proxy administrator for a medical devices company. You recently changed a pilot group of users from cloud app steering to all Web traffic. Pilot group users have started to report that they receive the error shown in the exhibit when attempting to access the company intranet site that is publicly available. During troubleshooting, you realize that this site uses your company's internal certificate authority for SSL certificates.
Which three statements describe ways to solve this issue? (Choose three.)
Answer : A, B, D
A . Import the root certificate for your internal certificate authority into Netskope:
This step ensures that Netskope recognizes and trusts SSL certificates issued by your company's internal certificate authority. By importing the root certificate, you enable proper SSL inspection and validation for internal sites.
B . Bypass SSL inspection for the affected site(s):
Since the intranet site uses your company's internal certificate authority, bypassing SSL inspection for this specific site allows users to access it without encountering SSL errors.
D . Change the SSL Error Settings from Block to Bypass in the Netskope tenant:
Adjusting the SSL Error Settings to ''Bypass'' allows users to proceed past SSL errors, including self-signed certificate errors. This ensures uninterrupted access to the intranet site.Reference:
Netskope Security Cloud Introductory Online Technical Training
Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Training
Netskope Cloud Security Certification Program
Question 7
You have enabled CASB traffic steering using the Netskope Client, but have not yet enabled a Real-time Protection policy. What is the default behavior of the traffic in this scenario?
Answer : B
In the scenario where CASB traffic steering is enabled using the Netskope Client without a Real-time Protection policy being activated, the default behavior of the traffic is to allow and log it (B). This means that the traffic will not be blocked; instead, it will be permitted to pass through and will be recorded for monitoring and analysis purposes. This default setting ensures visibility into the traffic and user activities without immediately enforcing a block, allowing for a period of observation and policy tuning before potentially more restrictive actions are taken1.
 All Official Question Types