Page: 1
/ 14
Total 91 questions
Palo Alto Networks Certified Detection and Remediation Analyst PCDRA Exam Questions
Question 1
Which version of python is used in live terminal?
Answer : D
Live terminal uses Python 3 with standard Python libraries to run Python commands and scripts on the endpoint. Live terminal does not support Python 2 or any custom or external Python libraries. Live terminal uses the Python interpreter embedded in the Cortex XDR agent, which is based on Python 3.7.4. The standard Python libraries are the modules that are included with the Python installation and provide a wide range of functionalities, such as operating system interfaces, network programming, data processing, and more. You can use the Python commands and scripts to perform advanced tasks or automation on the endpoint, such as querying system information, modifying files or registry keys, or running other applications.Reference:
Run Python Commands and Scripts
Python Standard Library
Question 2
In incident-related widgets, how would you filter the display to only show incidents that were ''starred''?
Answer : D
To filter the display to only show incidents that were ''starred'', you need to click the star in the widget. This will apply a filter that shows only the incidents that contain a starred alert, which is an alert that matches a specific condition that you define in the incident starring configuration.You can use the incident starring feature to prioritize and focus on the most important or relevant incidents in your environment1.
Let's briefly discuss the other options to provide a comprehensive explanation:
A) Create a custom XQL widget: This is not the correct answer. Creating a custom XQL widget is not necessary to filter the display to only show starred incidents. A custom XQL widget is a widget that you create by using the XQL query language to define the data source and the visualization type.You can use custom XQL widgets to create your own dashboards or reports, but they are not required for filtering incidents by stars2.
B) This is not currently supported: This is not the correct answer. Filtering the display to only show starred incidents is currently supported by Cortex XDR.You can use the star icon in the widget to apply this filter, or you can use the Filter Builder to create a custom filter based on the Starred field1.
C) Create a custom report and filter on starred incidents: This is not the correct answer. Creating a custom report and filtering on starred incidents is not the only way to filter the display to only show starred incidents. A custom report is a report that you create by using the Report Builder to define the data source, the layout, and the schedule.You can use custom reports to generate and share periodic reports on your Cortex XDR data, but they are not the only option for filtering incidents by stars3.
In conclusion, clicking the star in the widget is the simplest and easiest way to filter the display to only show incidents that were ''starred''. By using this feature, you can quickly identify and focus on the most critical or relevant incidents in your environment.
Filter Incidents by Stars
Create a Custom XQL Widget
Create a Custom Report
Question 3
An attacker tries to load dynamic libraries on macOS from an unsecure location. Which Cortex XDR module can prevent this attack?
Answer : D
The correct answer is D. Dylib Hijacking. Dylib Hijacking, also known as Dynamic Library Hijacking, is a technique used by attackers to load malicious dynamic libraries on macOS from an unsecure location. This technique takes advantage of the way macOS searches for dynamic libraries to load when an application is executed. To prevent such attacks, Palo Alto Networks offers the Dylib Hijacking prevention capability as part of their Cortex XDR platform.This capability is designed to detect and block attempts to load dynamic libraries from unauthorized or unsecure locations1.
Let's briefly discuss the other options to provide a comprehensive explanation:
A) DDL Security: This is not the correct answer. DDL Security is not specifically designed to prevent dynamic library loading attacks on macOS.DDL Security is focused on protecting against DLL (Dynamic Link Library) hijacking on Windows systems2.
B) Hot Patch Protection: Hot Patch Protection is not directly related to preventing dynamic library loading attacks.It is a security feature that protects against runtime patching or modification of code in memory, often used by advanced attackers to bypass security measures3. While Hot Patch Protection is a valuable security feature, it is not directly relevant to the scenario described.
C) Kernel Integrity Monitor (KIM): Kernel Integrity Monitor is also not the correct answer. KIM is a module in Cortex XDR that focuses on monitoring and protecting the integrity of the macOS kernel.It detects and prevents unauthorized modifications to critical kernel components4. While KIM plays an essential role in overall macOS security, it does not specifically address the prevention of dynamic library loading attacks.
In conclusion, Dylib Hijacking is the Cortex XDR module that specifically addresses the prevention of attackers loading dynamic libraries from unsecure locations on macOS. By leveraging this module, organizations can enhance their security posture and protect against this specific attack vector.
Endpoint Protection Modules
DDL Security
Hot Patch Protection
Kernel Integrity Monitor
Question 4
A Linux endpoint with a Cortex XDR Pro per Endpoint license and Enhanced Endpoint Data enabled has reported malicious activity, resulting in the creation of a file that you wish to delete. Which action could you take to delete the file?
Answer : C
The best action to delete the file on the Linux endpoint is to initiate Remediation Suggestions from the Cortex XDR console. Remediation Suggestions are a feature of Cortex XDR that provide you with recommended actions to undo the effects of malicious activity on your endpoints. You can view the remediation suggestions for each alert or incident in the Cortex XDR console, and decide whether to apply them or not. Remediation Suggestions can help you restore the endpoint to its original state, remove malicious files or processes, or fix registry or system settings. Remediation Suggestions are based on the forensic data collected by the Cortex XDR agent and the analysis performed by Cortex XDR.
The other options are incorrect for the following reasons:
A is incorrect because manually remediating the problem on the endpoint is not a convenient or efficient way to delete the file. Manually remediating the problem would require you to access the endpoint directly, log in as root, locate the file, and delete it. This would also require you to have the necessary permissions and credentials to access the endpoint, and to know the exact path and name of the file. Manually remediating the problem would also not provide you with any audit trail or confirmation of the deletion.
B is incorrect because opening X2go from the Cortex XDR console is not a supported or secure way to delete the file. X2go is a third-party remote desktop software that allows you to access Linux endpoints from a graphical user interface. However, X2go is not integrated with Cortex XDR, and using it would require you to install and configure it on both the Cortex XDR console and the endpoint. Using X2go would also expose the endpoint to potential network attacks or unauthorized access, and would not provide you with any audit trail or confirmation of the deletion.
D is incorrect because opening an NFS connection from the Cortex XDR console is not a feasible or reliable way to delete the file. NFS is a network file system protocol that allows you to access files on remote servers as if they were local. However, NFS is not integrated with Cortex XDR, and using it would require you to set up and maintain an NFS server and client on both the Cortex XDR console and the endpoint. Using NFS would also depend on the network availability and performance, and would not provide you with any audit trail or confirmation of the deletion.
Remediation Suggestions
Apply Remediation Suggestions
Question 5
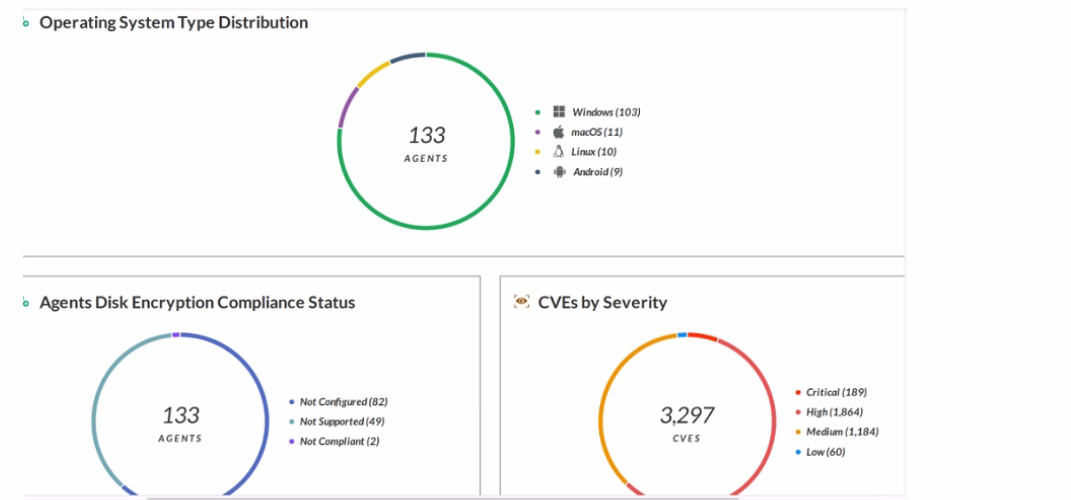
Which statement is correct based on the report output below?
Answer : C
The report output shows the number of endpoints that have forensic inventory data collection enabled, which is a feature of Cortex XDR that allows the collection of detailed information about the endpoint's hardware, software, and network configuration. This feature helps analysts to investigate and respond to incidents more effectively by providing a comprehensive view of the endpoint's state and activity. Forensic inventory data collection can be enabled or disabled per policy in Cortex XDR.Reference:
Forensic Inventory Data Collection
Cortex XDR 3: Getting Started with Endpoint Protection
Question 6
As a Malware Analyst working with Cortex XDR you notice an alert suggesting that there was a prevented attempt to download Cobalt Strike on one of your servers. Days later, you learn about a massive ongoing supply chain attack. Using Cortex XDR you recognize that your server was compromised by the attack and that Cortex XDR prevented it. What steps can you take to ensure that the same protection is extended to all your servers?
Answer : A
To ensure that the same protection is extended to all your servers, you need to create Behavioral Threat Protection (BTP) rules to recognize and prevent the activity. BTP is a feature of Cortex XDR that allows you to create custom rules that detect and block malicious or suspicious behaviors on your endpoints, such as file execution, process injection, network connection, or registry modification. BTP rules can use various operators, functions, and variables to define the criteria and the actions for the rules.By creating BTP rules that match the behaviors of the supply chain attack, you can prevent the attack from compromising your servers12.
Let's briefly discuss the other options to provide a comprehensive explanation:
B) Enable DLL Protection on all servers but there might be some false positives: This is not the correct answer. Enabling DLL Protection on all servers will not ensure that the same protection is extended to all your servers. DLL Protection is a feature of Cortex XDR that allows you to block the execution of unsigned or untrusted DLL files on your endpoints. DLL Protection can help to prevent some types of attacks that use malicious DLL files, but it may not be effective against the supply chain attack that used a Trojanized DLL file that was digitally signed by a trusted vendor.DLL Protection may also cause some false positives, as it may block some legitimate DLL files that are unsigned or untrusted3.
C) Create IOCs of the malicious files you have found to prevent their execution: This is not the correct answer. Creating IOCs of the malicious files you have found will not ensure that the same protection is extended to all your servers. IOCs are indicators of compromise that you can create to detect and respond to known threats on your endpoints, such as file hashes, registry keys, IP addresses, domain names, or full paths. IOCs can help to identify and block the malicious files that you have already discovered, but they may not be effective against the supply chain attack that used different variants of the malicious files with different hashes or names.IOCs may also become outdated, as the attackers may change or update their files to evade detection4.
D) Enable Behavioral Threat Protection (BTP) with cytool to prevent the attack from spreading: This is not the correct answer. Enabling BTP with cytool will not ensure that the same protection is extended to all your servers. BTP is a feature of Cortex XDR that allows you to create custom rules that detect and block malicious or suspicious behaviors on your endpoints, such as file execution, process injection, network connection, or registry modification. BTP rules can help to prevent the attack from spreading, but they need to be created and configured in the Cortex XDR app, not with cytool. Cytool is a command-line tool that allows you to perform various operations on the Cortex XDR agent, such as installing, uninstalling, upgrading, or troubleshooting. Cytool does not have an option to enable or configure BTP rules.
In conclusion, to ensure that the same protection is extended to all your servers, you need to create BTP rules to recognize and prevent the activity. By using BTP rules, you can create custom and flexible prevention rules that match the behaviors of the supply chain attack.
Behavioral Threat Protection
Create a BTP Rule
DLL Protection
Create an IOC Rule
[Cytool]
Question 7
When creating a custom XQL query in a dashboard, how would a user save that XQL query to the Widget Library?
Answer : D
To save a custom XQL query to the Widget Library, you need to click on ''Save to Widget Library'' in the dashboard and you will be prompted to give the query a name and description. This will allow you to reuse the query in other dashboards or reports. You cannot save a query to the Widget Library by clicking the three dots on the widget, as this will only give you options to edit, delete, or clone the widget. You also cannot save a query to the Action Center, as this is a different feature that allows you to create alerts or remediation actions based on the query results. You do not have to exit the dashboard and go into the Widget Library first to create a query, as you can do it directly from the dashboard.Reference:
Cortex XDR Pro Admin Guide: Save a Custom Query to the Widget Library
Cortex XDR Pro Admin Guide: Create a Dashboard
 All Official Question Types