Page: 1
/ 14
Total 108 questions
SailPoint Certified IdentityNow Engineer IdentityNow-Engineer Exam Questions
Question 1
Does the following use case correctly describe passthrough authentication?
Solution: A user logs into identityNow via an identity provider's login. The identity provider exchanges information via federation.
Answer : A
The use case describes a user logging into IdentityNow via an external identity provider's login, where information is exchanged via federation. This correctly aligns with the concept of passthrough authentication.
Passthrough authentication often uses protocols like SAML (Security Assertion Markup Language) or OAuth for federation. In this case, the identity provider (IdP) handles the authentication and then passes the necessary authentication tokens or assertions back to SailPoint IdentityNow, granting the user access without directly requiring their password to be stored or authenticated by IdentityNow. This is a typical use case of federation and passthrough authentication.
SailPoint IdentityNow Documentation on SAML and OAuth Federation.
SailPoint IdentityNow Federation and Passthrough Authentication Configuration Guides.
Question 2
Review the following transform:
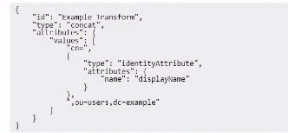
Can the following output of this transform be expected, based on the input provided in the option?
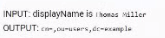
Solution:
Answer : A
The provided transform is of type 'Concat', which means it concatenates values from multiple sources. In this case, it appears to be concatenating the 'cn' value with the 'displayName' attribute of an identity. The 'type': 'IdentityAttribute' section specifies that the transform is pulling the 'displayName' attribute from the identity object.
Given the input where the displayName is 'Thomas Miller', the expected output is in the format cn=Thomas Miller,ou=users,dc=example, which aligns with the displayed output in the example. The transformation concatenates the displayName value with the rest of the distinguished name (DN), which is a common use case for generating a DN from user attributes.
Key Reference from SailPoint Documentation:
Concat Transform in IdentityNow: The concat transform is used to join multiple attribute values, and in this example, it successfully creates the expected DN string using the provided displayName input.
Question 3
Is this statement true about using the IdentityNow APIs?
Solution: API documentation is located at https://docs.sailpoint.com
Answer : A
SailPoint IdentityNow API documentation is indeed located at https://docs.sailpoint.com. This official documentation site contains all the information developers need to interact with IdentityNow through APIs. It includes guidelines on how to authenticate, make requests, and use the API endpoints to automate and integrate with other systems.
Key Reference from SailPoint Documentation:
SailPoint API Documentation: The site docs.sailpoint.com hosts the official API documentation for SailPoint IdentityNow, covering all aspects of using IdentityNow's APIs.
Question 4
Review the sentence below
The virtual appliance (VA) private key is_____.
Does this option correctly complete the sentence?
Solution: Stored both in the identityNow tenant and on the VA.
Answer : B
The virtual appliance (VA) private key is not stored in both the IdentityNow tenant and the VA. The VA private key, which is critical for secure communications, is stored only on the Virtual Appliance (VA) itself. It is used to authenticate and encrypt communications between the VA and the IdentityNow tenant. Storing such sensitive information in the IdentityNow tenant would violate best practices for key management and security.
Instead, the IdentityNow tenant only holds the public key or a reference to the key to facilitate secure exchanges with the VA. The private key remains secured locally within the VA, protecting it from potential security vulnerabilities associated with external storage.
SailPoint IdentityNow Virtual Appliance Architecture Guide.
SailPoint IdentityNow Security and Encryption Documentation.
Question 5
In an IdentityNow environment, the source lest connection is failing with a timeout error.
Is this a step an identityNow engineer should take to troubleshoot the problem?
Solution: Test connectivity from the virtual appliance (VA) to the source.
Answer : A
Testing connectivity from the virtual appliance (VA) to the source is a crucial troubleshooting step when dealing with connection issues such as timeouts. This can be done by accessing the VA and performing network tests (e.g., ping, telnet, or curl commands) to verify that the VA can communicate with the source over the required network paths. Ensuring that the VA has network access to the source can help identify if the problem is related to network configuration or firewall restrictions.
Key Reference from SailPoint Documentation:
VA to Source Connectivity Testing: Verifying network connectivity between the VA and the source is a fundamental step in diagnosing connection issues, as outlined in SailPoint's troubleshooting guidelines.
Question 6
Is the following true about custom connectors in IdentityNow?
Solution: Custom connector configurations can have account correlation settings defined.
Answer : A
Yes, custom connector configurations in SailPoint IdentityNow can have account correlation settings defined. Account correlation is used to link accounts from different sources to the correct identity in IdentityNow. When configuring a custom connector, it is possible to define how accounts from the connected system are correlated to existing identities based on attributes like usernames or other unique identifiers.
Key Reference from SailPoint Documentation:
Custom Connector Configuration: SailPoint allows for the definition of account correlation settings in custom connectors to ensure proper linking of external accounts to internal identities.
Question 7
Is the following description of an access profile correct?
Solution: It allows definition of an approval process.
Answer : A
Yes, an access profile allows the definition of an approval process. When an access profile is created, administrators can configure specific approval workflows that must be followed before the access is granted. This includes designating approvers or specifying multiple levels of approval, depending on the organization's policies. This capability is useful for ensuring that sensitive access requests are properly reviewed and approved.
SailPoint IdentityNow Access Request and Approval Workflow Guide.
SailPoint IdentityNow Access Profile Configuration Documentation.
 All Official Question Types