Page: 1
/ 14
Total 315 questions
Splunk Core Certified Power User SPLK-1002 Exam Questions
Question 1
Which of the following statements describe the search below? (select all that apply)
Index=main I transaction clientip host maxspan=30s maxpause=5s
Answer : A, B, D
The search below groups events by two or more fields (clientip and host), creates transactions with start and end constraints (maxspan=30s and maxpause=5s), and calculates the duration of each transaction.
index=main | transaction clientip host maxspan=30s maxpause=5s
The search does the following:
It filters the events by the index main, which is a default index in Splunk that contains all data that is not sent to other indexes.
It uses the transaction command to group events into transactions based on two fields: clientip and host. The transaction command creates new events from groups of events that share the same clientip and host values.
It specifies the start and end constraints for the transactions using the maxspan and maxpause arguments. The maxspan argument sets the maximum time span between the first and last events in a transaction. The maxpause argument sets the maximum time span between any two consecutive events in a transaction. In this case, the maxspan is 30 seconds and the maxpause is 5 seconds, meaning that any transaction that has a longer time span or pause will be split into multiple transactions.
It creates some additional fields for each transaction, such as duration, eventcount, startime, etc. The duration field shows the time span between the first and last events in a transaction.
Question 2
These users can create global knowledge objects. (Select all that apply.)
Answer : B, C
Question 3
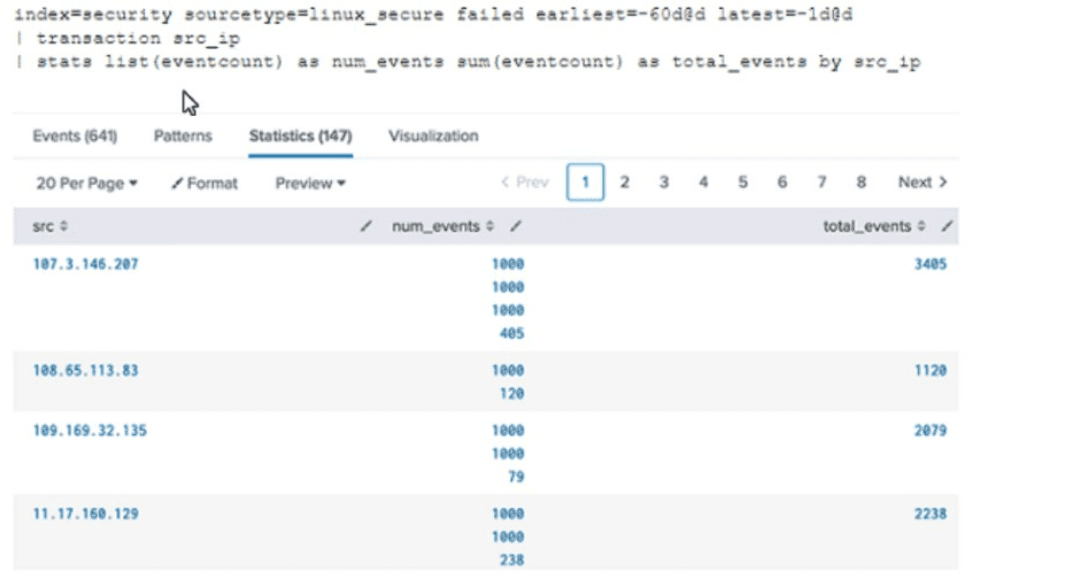
Why would the following search produce multiple transactions instead of one?
Answer : A
In Splunk, the transaction command is used to group events that share common characteristics into a single transaction1. By default, the transaction command groups all matching events into a single transaction1.
However, you can use the maxspan option to limit the time span of the transactions1. If the time span between the first and last event in a transaction exceeds the maxspan value, the transaction command will start a new transaction1.
Therefore, if the maxspan option is not included in the search, the transaction command might produce multiple transactions instead of one if the time span between the first and last event in a transaction exceeds the default maxspan value1.
Here is an example of how you can use the maxspan option in a search:
index=main sourcetype=access_combined | transaction someuniqefield maxspan=1h
In this search, the transaction command groups events that share the same someuniqefield value into a single transaction, but only if the time span between the first and last event in the transaction does not exceed 1 hour1. If the time span exceeds 1 hour, the transaction command will start a new transaction1.
Question 4
When creating a search workflow action, what character(s) are used as a placeholder for field values in the search string?
Answer : C
In workflow action definitions, field tokens are enclosed with dollar signs to represent field values dynamically.
Extract: ''In workflow actions, enclose field names with dollar signs ($fieldname$) to insert their values dynamically into URLs or searches.''
Question 5
Which of the following searches will show the number of categoryld used by each host?
Answer : B
Question 6
How do event types help a user search their data?
Answer : D
Event types allow users to assign labels to events based on predefined search strings. This helps categorize data and makes it easier to reference specific sets of events in future searches.
Splunk Docs - Event types
Question 7
A user wants a table that will show the total revenue made for each product in each sales region. Which would be the correct SPL query to use?
Answer : B
The chart command with sum(price) by product, region will return a table where the total revenue (price) is aggregated (sum) for each product and sales region. This is the correct way to aggregate data in Splunk.
Splunk Docs - chart command
 All Official Question Types