Page: 1
/ 14
Total 60 questions
The SecOps Group Certified Network Security Practitioner CNSP Exam Questions
Question 1
Which of the following is a valid DNS record type?
Answer : D
DNS (Domain Name System) records define how domain names are mapped to various types of data, each serving a specific purpose in network operations. The question asks for valid DNS record types, and all listed options are recognized.
Why D is correct:
A . NAPTR record: The Naming Authority Pointer (NAPTR) record is used for service discovery and mapping domain names to services, protocols, and ports (e.g., in SIP or ENUM systems).
B . SRV record: The Service (SRV) record specifies the hostname and port for specific services (e.g., LDAP, XMPP), aiding in service location.
C . TXT record: The Text (TXT) record stores arbitrary text data, often for SPF, DKIM, or domain verification.
All are valid DNS record types per RFC standards and CNSP documentation, making 'All of the above' the correct answer.
Why other options are incomplete: A, B, or C alone exclude other valid types listed, so D is the most comprehensive response.
Question 2
How many usable TCP/UDP ports are there?
Answer : B
TCP (Transmission Control Protocol) and UDP (User Datagram Protocol) port numbers are defined by a 16-bit field in their packet headers, as specified in RFC 793 (TCP) and RFC 768 (UDP). A 16-bit integer ranges from 0 to 65,535, yielding a total of 65,536 possible ports (2^16). However, port 0 is universally reserved across both protocols and is not considered 'usable' for standard network communication. According to the Internet Assigned Numbers Authority (IANA), port 0 is designated for special purposes, such as indicating an invalid or dynamic port assignment in some systems (e.g., when a client requests an ephemeral port). In practice, operating systems and applications avoid binding to port 0 for listening services, and it's often used in error conditions or as a placeholder in protocol implementations (e.g., socket programming).
Thus, the usable port range spans from 1 to 65,535, totaling 65,535 ports. These ports are categorized by IANA into:
Well-Known Ports (0--1023): Reserved for system services (e.g., HTTP on 80/TCP). Note that 0 is still reserved within this range.
Registered Ports (1024--49151): Assigned to user applications.
Dynamic/Ephemeral Ports (49152--65535): Used temporarily by clients.
From a security perspective, understanding the usable port count is critical for firewall configuration, port scanning (e.g., with Nmap), and detecting anomalies (e.g., services binding to unexpected ports). Misconfiguring a system to use port 0 could lead to protocol errors or expose vulnerabilities, though it's rare. The CNSP curriculum likely emphasizes this distinction to ensure practitioners can accurately scope network security assessments.
Why other options are incorrect:
A . 65536: This reflects the total number of possible ports (0--65535), but it includes the reserved port 0, which isn't usable for typical TCP/UDP communication. In security contexts, including port 0 in a count could lead to misconfigured rules or scanning errors.
C . 63535: This is an arbitrary number with no basis in the 16-bit port structure. It might stem from a typo or misunderstanding (e.g., subtracting 2000 from 65535 incorrectly), but it's invalid.
D . 65335: Similarly, this lacks grounding in protocol standards. It could be a miscalculation (e.g., subtracting 200 from 65535), but it doesn't align with TCP/UDP specifications.
Real-World Context: In penetration testing, tools like Nmap scan ports 1--65535 by default, excluding 0 unless explicitly specified (e.g., -p0-65535), reinforcing that 65,535 is the practical usable count.
Question 3
What user account is required to create a Golden Ticket in Active Directory?
Answer : D
A Golden Ticket is a forged Kerberos Ticket-Granting Ticket (TGT) in Active Directory (AD), granting an attacker unrestricted access to domain resources by impersonating any user (e.g., with Domain Admin privileges). Kerberos, per RFC 4120, relies on the KRBTGT account---a built-in service account on every domain controller---to encrypt and sign TGTs. To forge a Golden Ticket, an attacker needs:
The KRBTGT password hash (NTLM or Kerberos key), typically extracted from a domain controller's memory using tools like Mimikatz.
Additional domain details (e.g., SID, domain name).
Process:
Compromise a domain controller (e.g., via privilege escalation).
Extract the KRBTGT hash (e.g., lsadump::dcsync /user:krbtgt).
Forge a TGT with arbitrary privileges using the hash (e.g., Mimikatz's kerberos::golden command).
The KRBTGT account itself isn't 'used' to create the ticket; its hash is the key ingredient. Unlike legitimate TGTs issued by the KDC, a Golden Ticket bypasses authentication checks, persisting until the KRBTGT password is reset (a rare event in most environments). CNSP likely highlights this as a high-severity AD attack vector.
Why other options are incorrect:
A . Local User account: Local accounts are machine-specific, lack domain privileges, and can't access the KRBTGT hash stored on domain controllers.
B . Domain User account: A standard user has no inherent access to domain controller credentials or the KRBTGT hash without escalation.
C . Service account: While service accounts may have elevated privileges, they don't automatically provide the KRBTGT hash unless compromised to domain admin level---still insufficient without targeting KRBTGT specifically.
Real-World Context: The 2014 Sony Pictures hack leveraged Golden Tickets, emphasizing the need for KRBTGT hash rotation post-breach (a complex remediation step).
Question 4
Which is the correct command to change the MAC address for an Ethernet adapter in a Unix-based system?
Answer : A
In Unix-based systems (e.g., Linux), the ifconfig command is historically used to configure network interfaces, including changing the Media Access Control (MAC) address of an Ethernet adapter. The correct syntax to set a new MAC address for an interface like eth0 is ifconfig eth0 hw ether AA:BB:CC:DD:EE:FF, where hw specifies the hardware address type (ether for Ethernet), followed by the new MAC address in colon-separated hexadecimal format.
Why A is correct: The hw ether argument is the standard and correct syntax recognized by ifconfig to modify the MAC address. This command temporarily changes the MAC address until the system reboots or the interface is reset, assuming the user has sufficient privileges (e.g., root). CNSP documentation on network configuration and spoofing techniques validates this syntax for testing network security controls.
Why other options are incorrect:
B: hdw is not a valid argument; it's a typographical error and unrecognized by ifconfig.
C: hdwr is similarly invalid; no such shorthand exists in the command structure.
D: hwr is incorrect; the full keyword hw followed by ether is required for proper parsing.
Question 5
You are performing a security audit on a company's infrastructure and have discovered that the domain name system (DNS) server is vulnerable to a DNS cache poisoning attack. What is the primary security risk?
Answer : A
DNS cache poisoning, also known as DNS spoofing, involves an attacker injecting false DNS records into a resolver's cache, altering how domain names resolve.
Why A is correct: The primary risk is that an attacker can redirect users to malicious websites (e.g., phishing or malware sites) by poisoning the DNS cache with fake IP addresses. This can lead to credential theft, data exfiltration, or malware distribution. CNSP identifies this as the core threat of DNS cache poisoning, aligning with real-world attack vectors.
Why other option is incorrect:
B . Manipulate the cache of the web server or proxy server: This describes web cache poisoning, a different attack targeting HTTP caches, not DNS servers. DNS cache poisoning affects DNS resolution, not web or proxy server caches directly.
Question 6
Which one of the following is a phishing email?
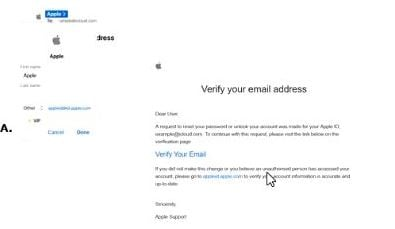
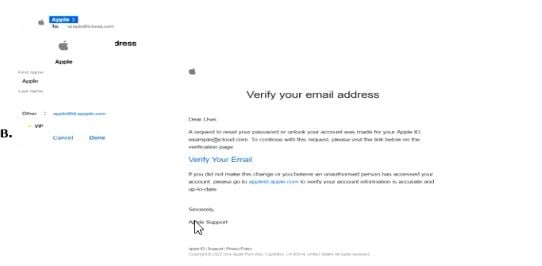
Answer : B
Question 7
Which of the following is true for SNMP?
A) The default community string for read-only access is "public."
B) The default community string for read/write access is "private."
Answer : C
SNMP community strings authenticate access, with defaults posing security risks if unchanged.
Why C is correct:
A: 'public' is the standard read-only default, per SNMP specs and CNSP.
B: 'private' is the standard read-write default, also per SNMP and CNSP.
Both are true, making C the answer.
Why other options are incorrect:
1, 2: Exclude one true statement each.
4: Both statements are true, so 'none' is wrong.
 All Official Question Types